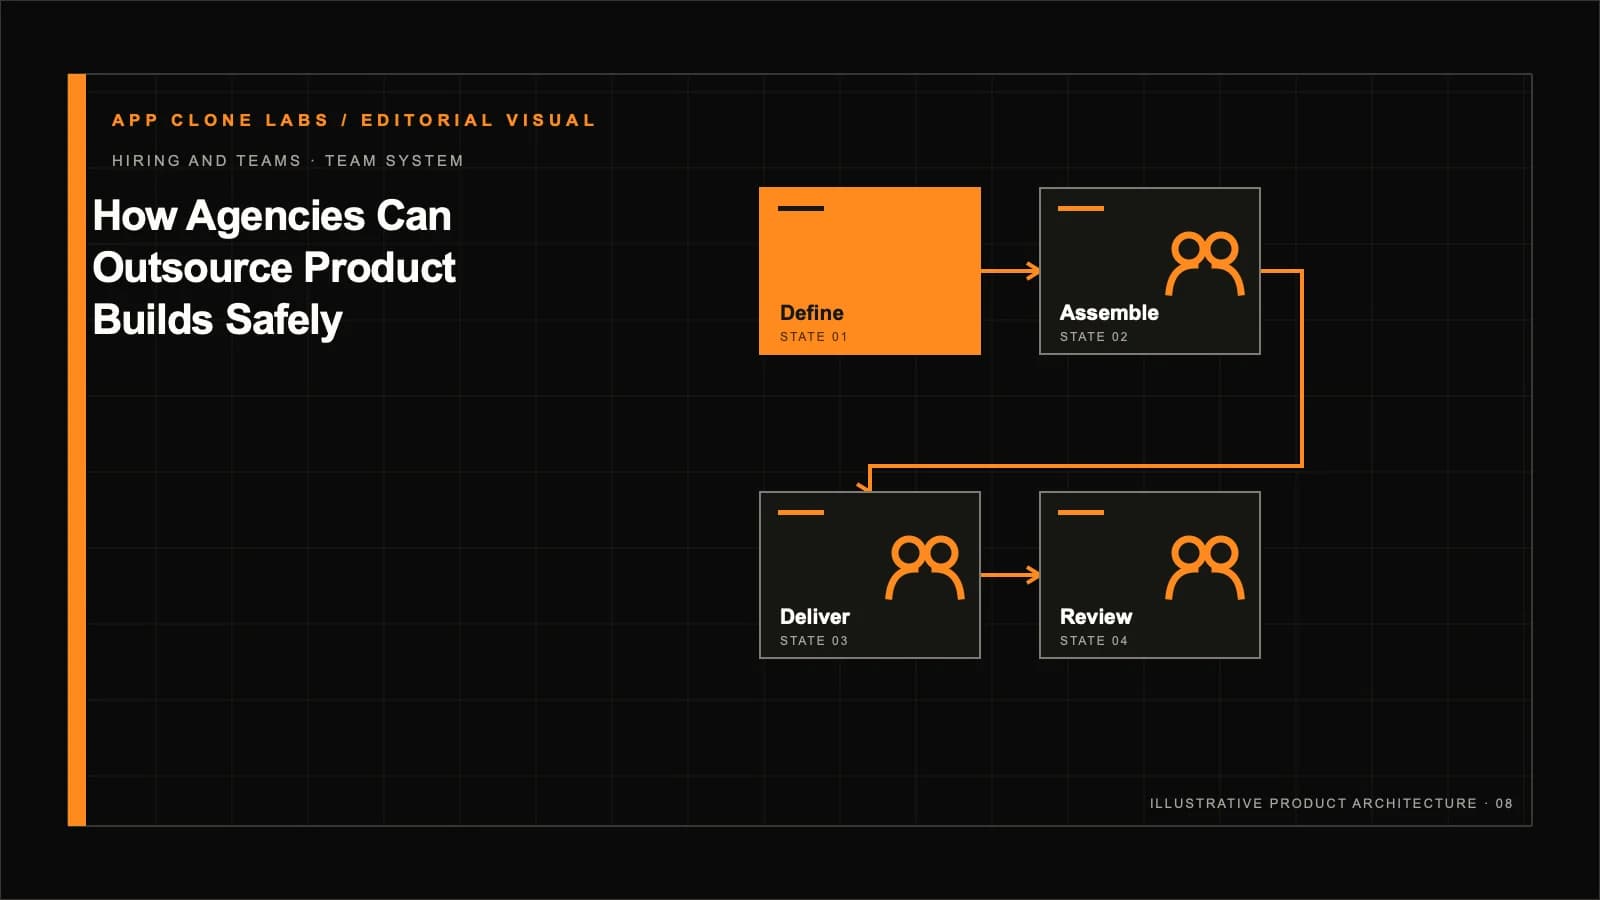
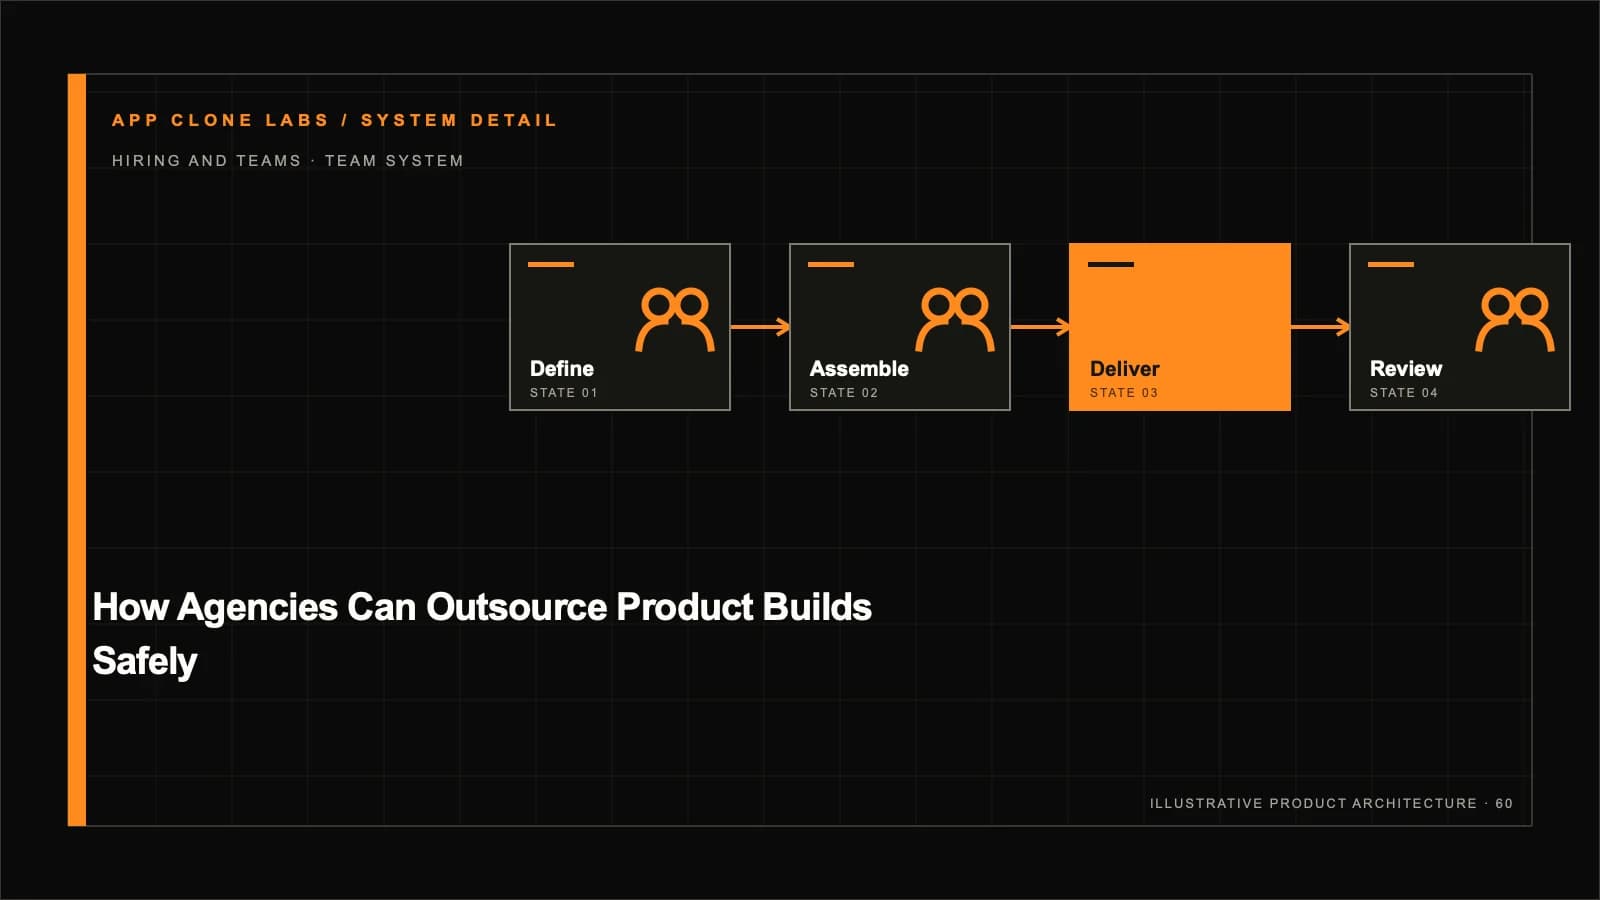
The client approves a booking prototype on Friday, but the delivery partner starts building a different cancellation rule on Monday. Both teams can point to a message that appears to authorize their interpretation. This hypothetical agency project has a decision problem before it has a coding problem. Outsourcing safely means giving each important decision an owner, an agreed record, and a way to resolve disagreement while the work is still inexpensive to change.
An agency can delegate implementation while retaining its client commitment. That requires more than a confidentiality agreement and a weekly demonstration. The operating arrangement must connect client consent, scope, commercial authority, repositories, data access, review, release, support, and exit. The following approach is a proposed delivery model, not a claim about any agency's existing contract or App Clone Labs client outcomes.
Confirm the client permits the delivery arrangement
Read the client agreement before selecting a partner. Determine whether subcontracting is permitted, whether named approval is required, which locations or organizations are restricted, and who can access confidential material. A white-label delivery arrangement does not remove the need to meet these obligations. Silence from a client is not a useful substitute for a required approval.
Prepare a clear description of the proposed arrangement. Explain which work the partner will perform, what information they need, who supervises them, and which responsibilities the agency retains. Where disclosure or approval is required, obtain it before sharing the material or starting that work. If a contract prohibits the intended model, revise the arrangement or the agreement through the appropriate authorized process.
Keep the client-facing promise aligned with the delivery reality. Do not sell an entirely in-house team while relying on an external partner in a way that contradicts the representation. The commercial model can remain confidential within agreed boundaries, but responsibility and required disclosure should be explicit. The developer engagement overview can help distinguish a managed delivery relationship from hiring individual contributors.
Bound the outcome in a reviewable statement of work
A useful scope describes a user journey, its operating rules, and its acceptance evidence. For a hypothetical booking product, specify how a customer requests a slot, receives confirmation, reschedules, cancels, and obtains support. Identify who supplies content, payment configuration, business policy, and third-party accounts. These dependencies change both the estimate and the date at which work can be accepted.
Define deliverables beyond screens. They may include source code, database changes, automated checks, environment configuration, release notes, operating instructions, and a handover session. State supported platforms, representative devices, accessibility requirements, and excluded integrations. An apparently complete interface can still be unusable if the agreed administrator workflow or failure recovery has never been implemented.
Avoid using a competitor's product as the entire specification. It can establish category context, but it cannot settle your client's pricing rules, data rights, refund handling, or operating roles. Capture those choices in the project record. If discovery remains incomplete, purchase a bounded discovery phase with defined outputs rather than pretending the entire build is already a fixed and understood obligation.
Name the people allowed to decide
The agency should retain an accountable client lead and an authorized product decision maker. The partner needs a delivery lead who can commit its implementation work. Name who approves architecture, design interpretation, security exceptions, scope changes, release, and acceptance. One person can hold several roles, but each decision should have a visible route when that person is absent.
For example, a partner may propose that cancellation fees are calculated in the mobile client. Its engineer can recommend an approach; the agency's technical owner should approve the trust boundary, and the client's authorized owner should approve the business policy. A project manager's request to speed up a demonstration should not quietly replace either decision.
Maintain a short decision log with context, choice, approver, and affected work. Link an implementation task to the relevant decision rather than copying conflicting instructions into several tools. For teams lacking technical leadership, CTO services describes one possible support model. Whatever the staffing arrangement, the agency still needs enough competence to review what it is accepting.
Verify a partner through a bounded delivery sample
Use a small paid discovery or implementation stage to examine collaboration before delegating the whole product. This is a recommendation, not a report of a company screening policy. A useful sample crosses one real boundary: a booking request reaches a test service, returns a confirmed result, and handles a timeout without creating duplicate reservations.
Evaluate the proposed team rather than only a sales presentation. Ask who will implement, who reviews, how substitutions work, and what evidence of prior work they are authorized to share. Do not require confidential client repositories or accept screenshots as proof of source ownership. A sanitized technical walkthrough can reveal how the team reasons about tests, releases, and recovery.
Review the sample's repository, assumptions, test evidence, and unresolved questions. A team that identifies a missing product decision early may be more useful than one that hides uncertainty until acceptance. The stage should end with a choice to proceed, revise scope, or stop, with usable artifacts and agreed payment treatment regardless of whether the larger engagement continues.
Establish source and asset ownership before reuse
Separate newly commissioned work, the partner's pre-existing components, open-source dependencies, and client-provided materials. Agree the rights required to operate, modify, transfer, and maintain each category. Assignment language alone may not cover a licensed template, commercial SDK, font, or stock image. Identify recurring costs and restrictions before the client becomes dependent on them.
Ask the partner to document material third-party components and their licence obligations. If a reusable internal module will remain partner-owned, define the client's licence and what happens when support ends. If source must be supplied, name which source and build materials are included. A compiled artifact without the corresponding build inputs may be insufficient for the maintenance arrangement the agency sold.
White-label branding also needs boundaries. Decide whether the partner may mention the engagement, use screenshots, contact the end client, or include attribution. Obtain any required permissions for portfolios and case studies separately. Do not describe another client's outcome as evidence for this project or import their private assets into a new build simply because the visual structure is similar.
Put repositories and access under accountable control
Choose the repository owner and organization at the start. The client or agency should have the access required by the agreement throughout delivery, rather than receiving a final archive only after the relationship deteriorates. Include issue history, review discussions, and build configuration in the handover expectations because they explain decisions that source files alone cannot.
Use individual accounts, least privilege, and a clear invitation and removal process. Separate permission to propose changes from permission to approve and release them. GitHub's protected branch documentation describes controls for reviews, required checks, and restrictions, including possible administrator bypasses. Configure the actual repository and verify behaviour rather than assuming a platform feature is enabled.
Never share a single owner password with every contractor. Give scoped service identities to automation and record who manages them. When a partner engineer changes, remove the old access and review active tokens, integrations, and assigned work. Team membership on a chat channel does not prove that repository, cloud, and support access have changed with it.
Separate environments and minimize shared client data
Build and test with synthetic data where possible. The partner should not need a production database merely to implement a booking form. Supply representative edge cases, including unusual names, timezone boundaries, empty accounts, and cancellation states. A tiny unrealistic dataset creates testing gaps, but that does not justify copying unrestricted customer records into a developer laptop.
Document development, test, staging, and production environments, their owners, and their allowed users. Make their identities obvious in the interface and deployment tooling. Separate credentials and external-service accounts so a test refund or notification cannot reach a real customer accidentally. When a sandbox is imperfect, state the remaining risk and choose a controlled test procedure.
Secrets should reach authorized workloads through the agreed secret-management mechanism, not public issues, screenshots, or ordinary project chat. Review logging and diagnostic exports for private information. The OWASP authorization guidance recommends checking permissions for each request and applying least privilege. Translate that into application tests as well as project access rules; protecting the repository does not protect a poorly authorized customer endpoint.
Map subprocessors and privacy responsibilities explicitly
Identify whether the work involves personal data and which parties decide its purposes or process it under instructions. These roles follow the actual activity and applicable rules, not merely the label subcontractor. The EDPB's controller and processor explanation explains those distinctions and the requirement for written authorization when appointing a subprocessor under the GDPR framework.
For an engagement to which those requirements apply, have the responsible privacy and legal owners confirm the processing arrangement before data access. Record the partner, locations, services used, information involved, permitted purpose, retention, and incident contact. Do not treat a general confidentiality clause as a substitute for the processing terms and authorizations the situation requires.
Include the partner's tools in the review. Error monitoring, support systems, file sharing, analytics, and AI coding services may receive client material depending on configuration and use. Approve the allowed tools and data categories, define restrictions, and create a route for proposed changes. A developer should know whether a private log excerpt may be pasted into a tool before the incident that creates pressure to do so.
Stage delivery around integrated outcomes
An early stage should prove the project can build and deploy into the agreed test environment. The next should prove one complete journey with the real data boundaries and a representative integration. Later stages can expand coverage. This exposes account, infrastructure, and contract problems while there is still time to adjust the plan.
Accept a demonstrated outcome with identified evidence. A recording of a happy-path prototype is not equivalent to an accessible test environment, reviewable source, and reproducible checks. Require the partner to state what is mocked, which dependencies are unavailable, and which known issues remain. The agency should pass that clarity through to the client rather than presenting every intermediate demo as production-ready software.
Link payments to agreed milestones and review periods where the commercial model supports it. Define how disputed acceptance, client delays, and approved partial delivery are handled. A fixed-price stage can still need a change process; time-based work can still need observable outcomes. Avoid creating incentives to conceal defects simply because an invoice depends on calling the entire product finished.
Make QA a shared release discipline
The partner should verify its work before requesting agency acceptance. The agency should perform an independent review appropriate to the product and risk, rather than merely forwarding the partner's test summary. Name the environments, data, device coverage, and test accounts used. Record the release candidate so a passed report can be tied to the artifact actually delivered.
Use security and accessibility requirements that can be inspected. NIST's SSDF version 1.1 provides a secure-development practice framework; WCAG 2.2 provides testable web accessibility criteria. Select relevant requirements and evidence for the work. Citing either source does not establish certification, full conformance, or the absence of defects.
For the hypothetical booking flow, test two people requesting the last slot, a delayed payment result, a withdrawn staff permission, and a keyboard user correcting a form error. Include dependency outages and operator recovery. These scenarios connect verification to business consequences. A test count alone says little if every check repeats a simple input rule and none exercises the boundary that can lose a reservation.
Keep progress visible without turning reporting into theatre
A weekly review should answer what became usable, what evidence supports that claim, what is blocked, and which decision is needed next. Show working software and the corresponding changes. Keep unfinished work visible. A percentage complete without an agreed denominator often disguises the hardest integration work as a small remainder.
Use a shared backlog with clear priority and an owner for questions. The client may communicate through the agency, but the partner needs timely access to clarified decisions. Set an expected response window and a fallback when a decision stalls. Waiting for an answer should appear as a dependency with consequences, not as unreported lost time blamed on either team after the deadline.
Measure rework causes, unresolved severe defects, review delays, and the age of blocked decisions. Use those measures to improve the arrangement rather than rank individuals from incomplete information. A partner producing many commits may still be building against obsolete instructions. A quieter week that resolves a critical integration assumption can be valuable if the outcome and next action are documented.
Control changes where the promise changes
Create a lightweight change record when a request affects scope, acceptance, cost, dates, data handling, or operational responsibility. State the request, affected behaviour, options, estimated consequence, and authorized decision. A minor text correction may not need a commercial amendment, while a new refund policy can change code, tests, support, and finance reconciliation.
Suppose the client asks for same-day rescheduling after implementation begins. In this hypothetical scenario, the agency should identify capacity checks, provider notices, price adjustments, and cancellation interactions before asking the partner to add a button. The client can then choose a narrower rule or approve the additional work. Preserve the accepted baseline so disagreement does not depend on whose memory of a call sounds more confident.
Distinguish a defect from a new request through the agreed acceptance criteria. If the product fails a documented rule, fixing it belongs to the applicable defect arrangement. If the client changes the rule, evaluate the change openly. Avoid making the partner absorb every ambiguity or making the client pay again for behaviour already promised; both practices create incentives to avoid clear records.
Separate release approval from build completion
A build can pass testing while the organization is not ready to operate it. Confirm production accounts, support coverage, monitoring, backup recovery, migration plans, and user communications. Name who can authorize release and who can stop it. The partner may execute the deployment without owning the business decision to expose the new behaviour to customers.
The CI/CD launch guide expands build and deployment controls. For the agency arrangement, tie each release to an artifact, approved changes, check results, and recovery plan. If a database migration cannot simply be reversed, define how to contain failure and preserve data rather than promising a rollback button that does not exist.
Rehearse an incident across the organizational boundary. A hypothetical deployment causes duplicate confirmation messages. Who pauses the sender, investigates affected records, informs the agency, and decides what the client tells users? Agree response responsibilities and contact coverage in advance. Describe an actual support commitment rather than assuming an engineer who built the feature is always available after delivery.
Rehearse handover while the partner is still present
Ask another authorized engineer to build and run the product from the delivered instructions. Have them deploy a test release, find the important configuration, restore a test backup, and trace a user request through diagnostics. The partner should observe and fill gaps. This reveals missing knowledge more effectively than accepting a large documentation folder no one has attempted to use.
The handover should identify source and asset rights, dependencies, accounts, environment ownership, recurring costs, release steps, monitoring, known defects, and outstanding decisions. Include a system map small enough to remain useful and references to deeper detail where needed. Configuration and credentials require secure transfer, with rotation or replacement where appropriate; do not place every secret in the handover document.
Agree the post-handover warranty or support boundary, including exclusions and escalation. The post-launch support checklist helps define ongoing ownership. A dedicated team may retain maintenance responsibility, while staff augmentation may place it inside the agency. Neither label answers who handles the next serious defect without a concrete agreement.
Keep an exit path that works before a dispute
Plan for ordinary personnel change as well as contract termination. A partner's lead engineer may become unavailable while the relationship remains healthy. Require a current secondary contact, reviewable work in progress, and enough shared knowledge for another engineer to continue. The agency should apply the same discipline to its own product and client leads; losing the only person authorized to answer questions can block delivery just as effectively as losing a programmer.
Review concentration risk at each milestone. If the only working build exists on a private machine, the only deployment credential belongs to an individual, or the only explanation of a migration lives in a meeting recording, assign a correction before expanding scope. The correction may be a short rehearsal or an account transfer rather than another document. Continuity improves when the next person can perform the work, not merely when the current owner promises to remain reachable.
Define termination notice, work-in-progress delivery, final reconciliation, transition assistance, data return or deletion, and access removal. Have the responsible legal and commercial owners settle applicable terms. The operating team should then be able to execute them without asking the departing partner for information only they possess. An exit clause with no repository or account access is difficult to use.
Test a controlled replacement scenario before the project becomes dependent on one person. Can the agency assign a new maintainer, access the current release, and identify unfinished tasks? Can the partner remove its personnel without deleting shared resources or interrupting production? Keep the transition inventory current at milestones so exit preparation is part of delivery rather than an emergency reconstruction.
After exit, confirm the agreed access revocations, outstanding obligations, and treatment of retained records. Preserve project evidence needed for accepted operations and disputes under the approved policies. Record any unresolved handover limitation and its owner. The agency's client commitment continues, so the final question is practical: can the authorized replacement team operate and change the product with the materials it now controls?
Implementation references
Further reading: OWASP API Security Top 10.
Further reading: NIST Cybersecurity Framework 2.0.
Frequently asked questions
Does white-label outsourcing mean the client cannot know the partner?
No. Branding and client-contact boundaries are separate from contractual disclosure and privacy obligations. Follow the client agreement and obtain required consent before the relevant work or access begins. Avoid representations about an in-house team that conflict with delivery reality. State the permitted communication and attribution arrangement explicitly.
Who should own the repository during the build?
Choose the owner according to the client agreement and ensure the agency or client has the access needed throughout delivery. Do not rely on a final archive as the only continuity mechanism. Include review history, build configuration, dependencies, and pending work in the handover expectations, not merely the application source files.
Can the partner use production data for development?
Only through an authorized arrangement that justifies and controls that access. Prefer realistic synthetic data for ordinary implementation. When real data is necessary, confirm purpose, scope, security, retention, locations, and applicable processing terms with the responsible owners. A confidentiality agreement alone does not decide every privacy or contractual requirement.
How should the agency handle a client request sent directly to the partner?
The partner can capture and clarify it, but material changes should follow the authorized decision route. Record its effect on scope, dates, cost, tests, and operations before treating it as approved. Agree whether direct client discussion is permitted and how decisions return to the shared project record so the agency does not lose accountability.
What should be accepted at an intermediate milestone?
Accept the defined integrated outcome with identified source, test evidence, known limitations, and environment access. Separate a useful prototype from production readiness. If an external dependency is mocked, say so and assign the remaining integration. The commercial milestone should make these distinctions visible rather than encouraging a broad and unsupported claim of completion.
Is an NDA enough to protect source and client assets?
An NDA concerns confidentiality; it does not by itself settle ownership, licences, reuse, transfer rights, or recurring third-party costs. Specify commissioned work, pre-existing components, open-source obligations, and client-provided materials. Have the responsible commercial or legal owner confirm the agreement matches the rights needed to maintain and transfer the product.
What is the strongest handover test?
Have an authorized replacement engineer build, deploy, diagnose, and recover a test environment using the delivered materials. Observe where they need undocumented help, then correct those gaps before the partner leaves. A successful rehearsal provides more useful evidence than the size of a document bundle or a promise that support can answer questions later.
Comparison register
Agency controls that preserve client accountability
| Delivery boundary | Fragile arrangement | Reviewable agreement or evidence |
|---|---|---|
| Client consent | Assume white-label means no disclosure | Confirm subcontracting approval and representation requirements before access |
| Decision ownership | Any chat message changes the build | Named approver and shared decision record for scope and policy |
| Source continuity | Final archive after completion | Agreed repository access, rights, build inputs and current work throughout delivery |
| Acceptance | Prototype recording and completion percentage | Identified integrated outcome, artifact, environment and QA evidence |
| Exit readiness | Documentation promised at termination | Replacement engineer rehearses build, deployment and recovery before handover |
- 01
- 02
- 03
- 04
- 05
- 06
- 07
- 08
- 09
Reviewed by Aditya Bhimrajka
This guide is written for founders and operators planning clone-inspired platforms, SaaS products, marketplaces, and mobile apps. It is reviewed against App Clone Labs delivery patterns, product scoping standards, and current implementation realities before being published.
Review the editorial team structureRelated product paths
Continue with the services, solutions, guides, and articles that connect this topic to a real software build.