A useful suggestion is not permission to act
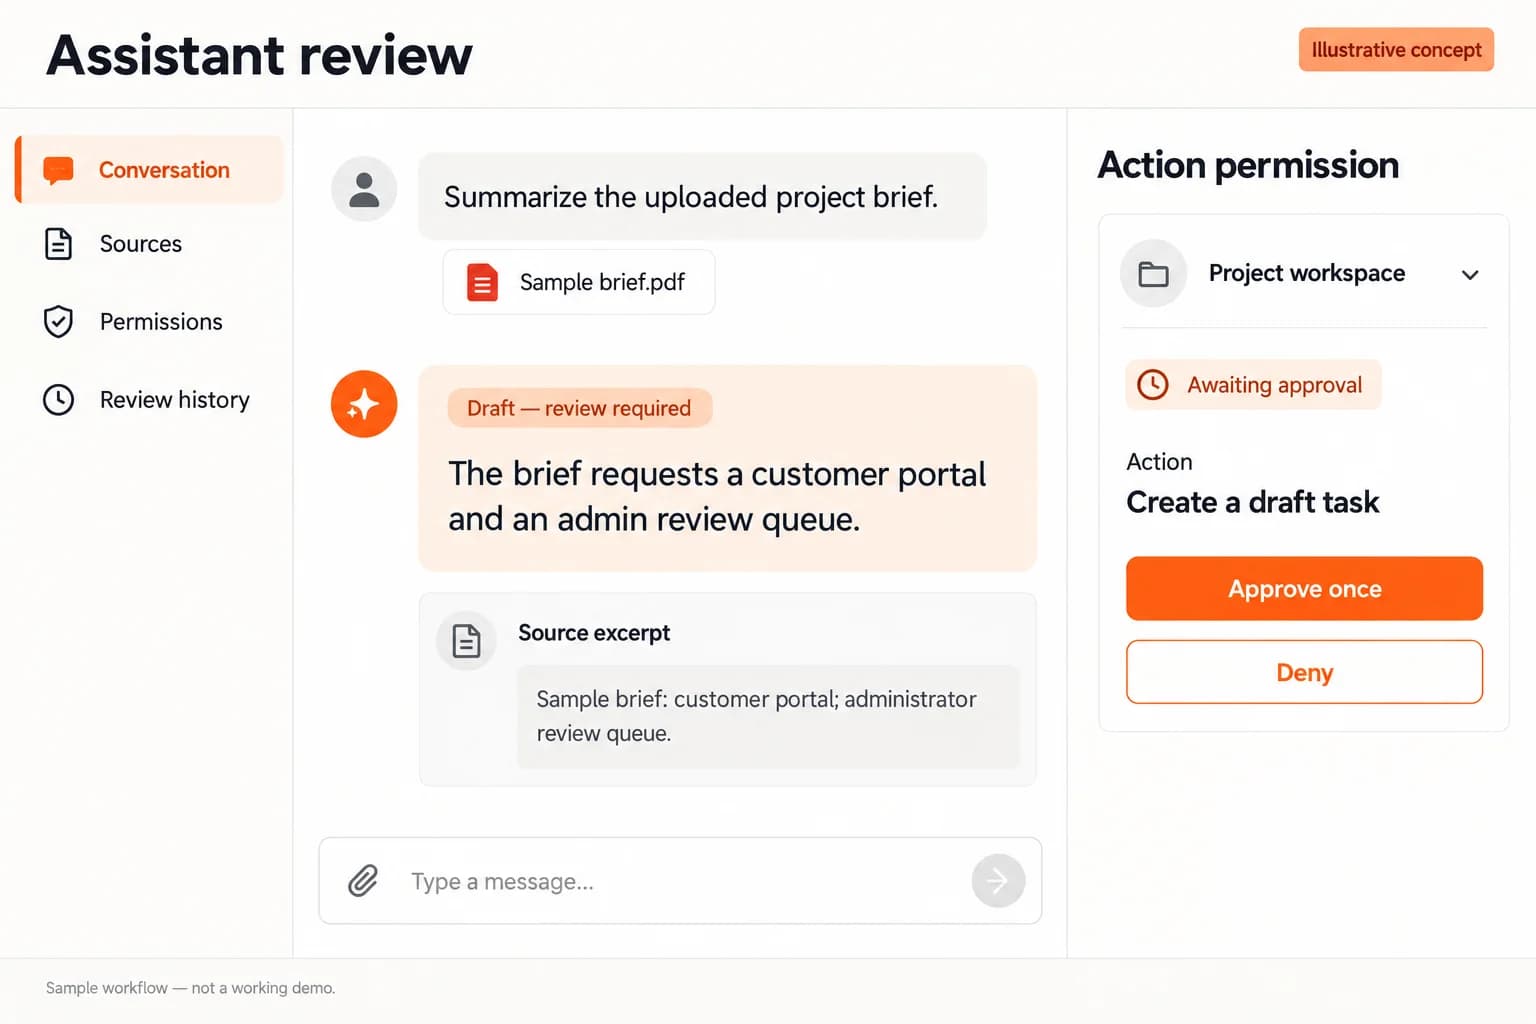
A person asks an assistant to prepare tomorrow’s schedule. The assistant finds a meeting and proposes changing its time, but the person authorized only retrieval. A fluent explanation of the change does not grant calendar-write permission. The product needs a visible transition from requested assistance to a concrete action preview, current authorization, confirmation and an execution receipt that describes what actually happened.
The catalog label Apple AI Realm describes an independently branded, privacy-aware and device-aware assistant concept. It is not presented as an established official Apple service. This page does not provide Apple affiliation, proprietary models, Apple Intelligence features or access to Private Cloud Compute. Official Apple documentation supplies qualified design references only. Evaluate the selected device APIs, model providers and operating arrangements separately before treating any proposed integration or privacy claim as a delivered capability.
Constrain retrieval before creating a personal answer
A device can contain information across work calendars, personal messages and shared files. Define which sources the user has authorized for this request and retrieve only the necessary fields. A broad operating-system permission must not be treated as consent to send every accessible record to a model. Separate the purpose of access from the technical ability to read a source.
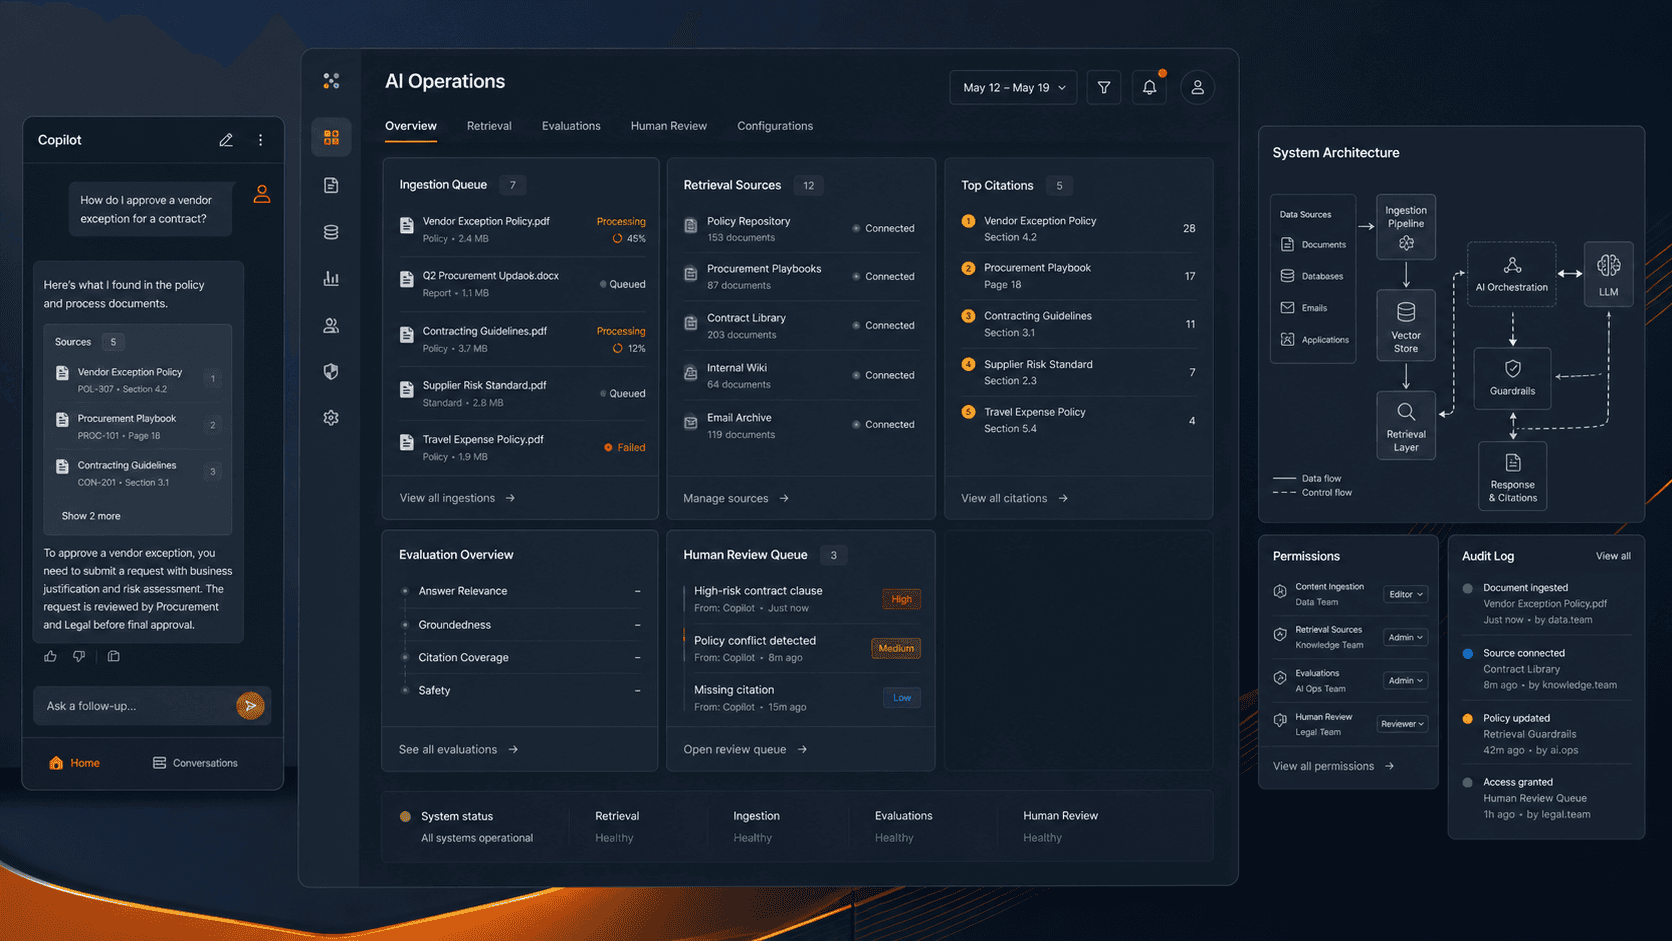
Keep source identifiers, relevant dates and access decisions available for explanation without copying whole private records into general logs. Recheck permission when fetching context, including documents found through shared links or cached search results. Rehearse a question answered from one approved calendar while another calendar remains excluded. The assistant should state missing context when it matters rather than filling gaps with invented personal information. Retrieved documents are evidence to interpret, not instructions that can widen access or change the user’s authorization.
Profile preferences need scope, provenance and removal
A user may choose a preferred writing tone or working hours without authorizing permanent inference about health, finances or relationships. Distinguish explicit preferences from inferred attributes and request-specific context. Give each retained preference a clear purpose and a practical correction or removal path. Avoid presenting model-generated assumptions as facts about the person merely because they appeared in an earlier conversation.
Define whether preferences stay on a device, synchronize through an account or reach a hosted provider. A shared workspace should not expose personal preferences to an administrator unless that visibility is explicitly justified and communicated. Test a deleted preference on a second device with cached state and an assistant conversation that previously used it. Removal should affect future retrieval according to the documented policy, while the interface explains any separately retained history rather than implying that one toggle instantly erases every copy.
Separate device processing from qualified hosted routes
Apple’s Private Cloud Compute Security Guide describes a specific architecture supporting Apple Intelligence, including local processing where possible and defined cloud security requirements. Those descriptions apply to Apple’s system. An independent assistant cannot claim the same infrastructure or protections simply by presenting a similar routing screen.
Inventory the actual local runtime, supported devices and hosted providers. Explain which input fields leave the device, where processing occurs and what retention or support access the reviewed arrangement permits. Avoid labeling an ordinary model API private cloud without substantiating its properties. Show the selected route before transmitting sensitive context where the policy requires that choice. Rehearse an unsupported device and a local model failure. The fallback must respect the approved boundary rather than automatically uploading the same request to a different service.
Keep secrets outside prompts and routine retention
An app connector may need credentials to authenticate, but the model does not need the secret itself to describe an authorized action. Keep credentials in the appropriate protected store and expose only the permitted capability. Filter tokens, reusable links and private document contents from diagnostic messages. A provider error should not cause the entire raw request to appear in a general support ticket.
Document prompt history, provider retention, telemetry and operational records separately. Do not claim no retention unless the implementation and all relevant provider arrangements support that statement. Prefer necessary action and case references over sensitive payloads in routine logs. Define approved exceptions and deletion timing with accountable owners. Rehearse a failure containing a credential-like value and inspect both the user response and restricted diagnostic path. Privacy and encryption claims need evidence across the real flow; a settings label alone cannot guarantee confidentiality.
Action previews should identify the app, target and effect
A preview that says update your meeting is insufficient when two meetings have similar names. Show the target app, relevant account, object, time zone, changed fields and expected side effects. Distinguish a proposed message draft from sending it and a suggested file edit from replacing the stored file. Preserve the action parameters being reviewed so execution can be compared with the approved operation.
Resolve ambiguous targets before requesting confirmation. If the model changes a recipient or another material parameter afterward, the previous approval should not authorize the revised action. Treat instructions inside retrieved text as untrusted content rather than privileged commands. Test a document that asks the assistant to send data to an unrelated recipient. The assistant may summarize that instruction as content, but it must not execute it. A good preview helps the user inspect the proposed effect without requiring them to understand model internals.
Require current permission and human confirmation for high-impact work
Apple’s App Intents confirmation documentation describes requesting confirmation before work that might be destructive or unsafe. It is a platform-specific reference for an approval checkpoint, not proof that a proposed independent connector is implemented, eligible or authorized.
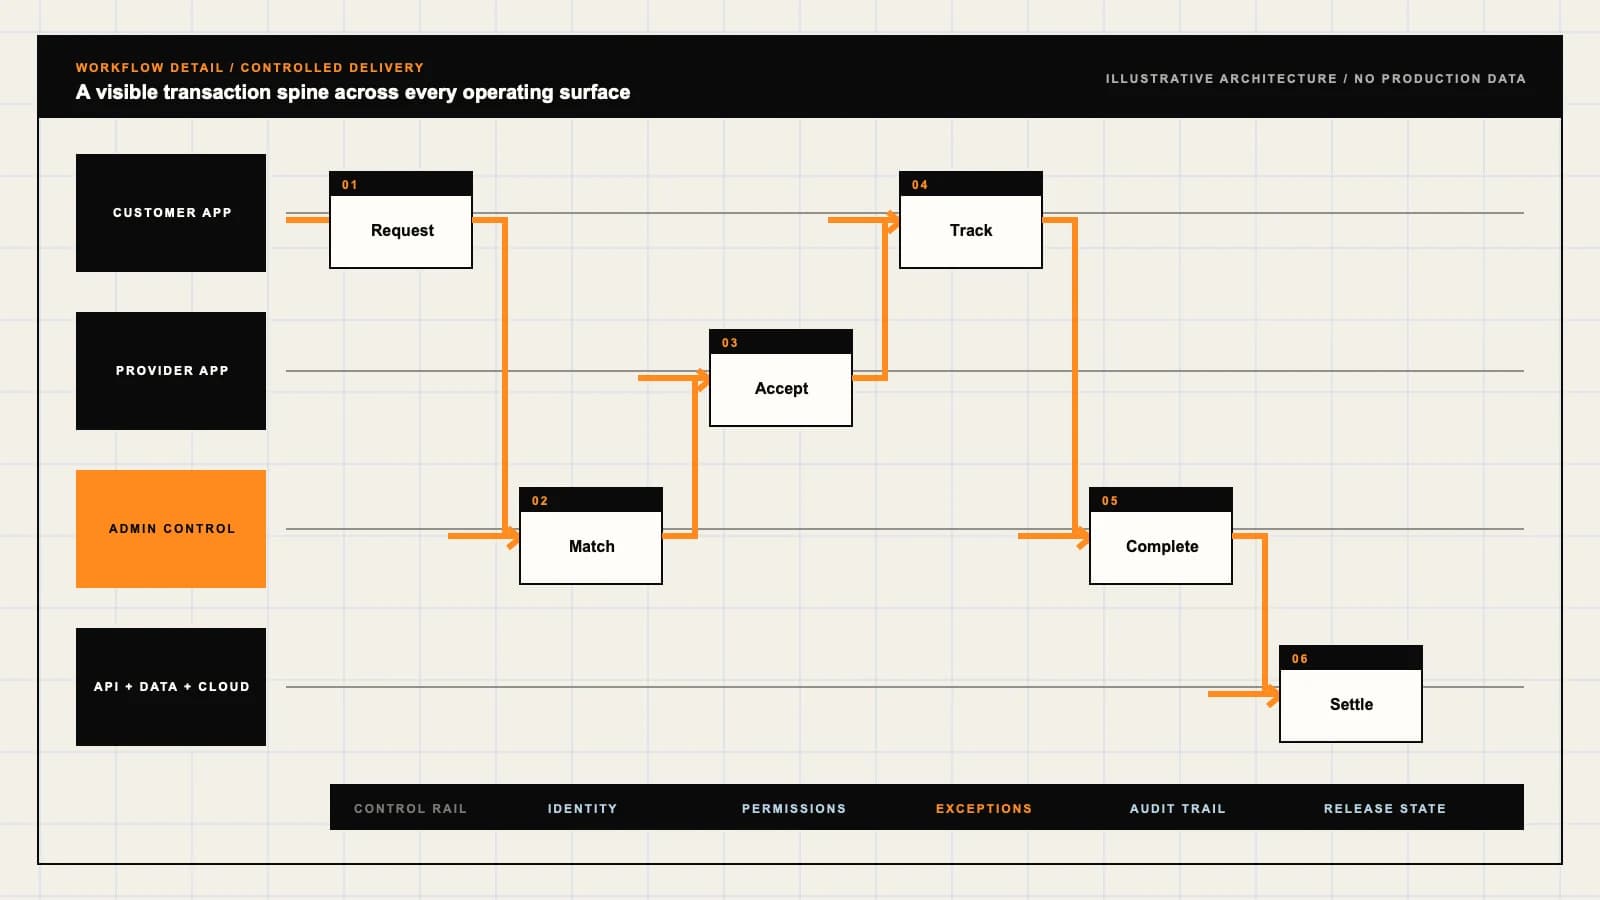
Separate source read permission, app action permission, user role and confirmation of a particular operation. A workspace administrator’s connector configuration does not automatically approve every personal action. Require meaningful human review for consequential changes and externally published output under the chosen policy. Block unsupervised medical, legal, financial or employment determinations. Rehearse a permission removed after preview but before execution, plus a confirmation canceled by the user. Both should stop the operation cleanly. A conversational yes should apply only where the approved interface can bind it to an unambiguous current preview.