A transfer is ready when the selected bundle is committed
A designer selects five print files, watches the progress reach completion and sends the download link. One file is still waiting for validation, while the archive contains only four. The recipient begins printing from an incomplete package. A simple transfer service needs a defensible ready state based on the selected bundle, not an upload animation that ends before the delivery record is complete. The sender should see what remains unresolved before sharing.
A WeTransfer-style build here means independently branded temporary file sending with email notices and recipient links. It supplies neither WeTransfer affiliation nor its software, accounts, storage contracts or customer network. Choose the first file types, sender model and retention terms before adding presentation features. Occasional sending should remain understandable without silently becoming a shared workspace or a promise of permanent storage.
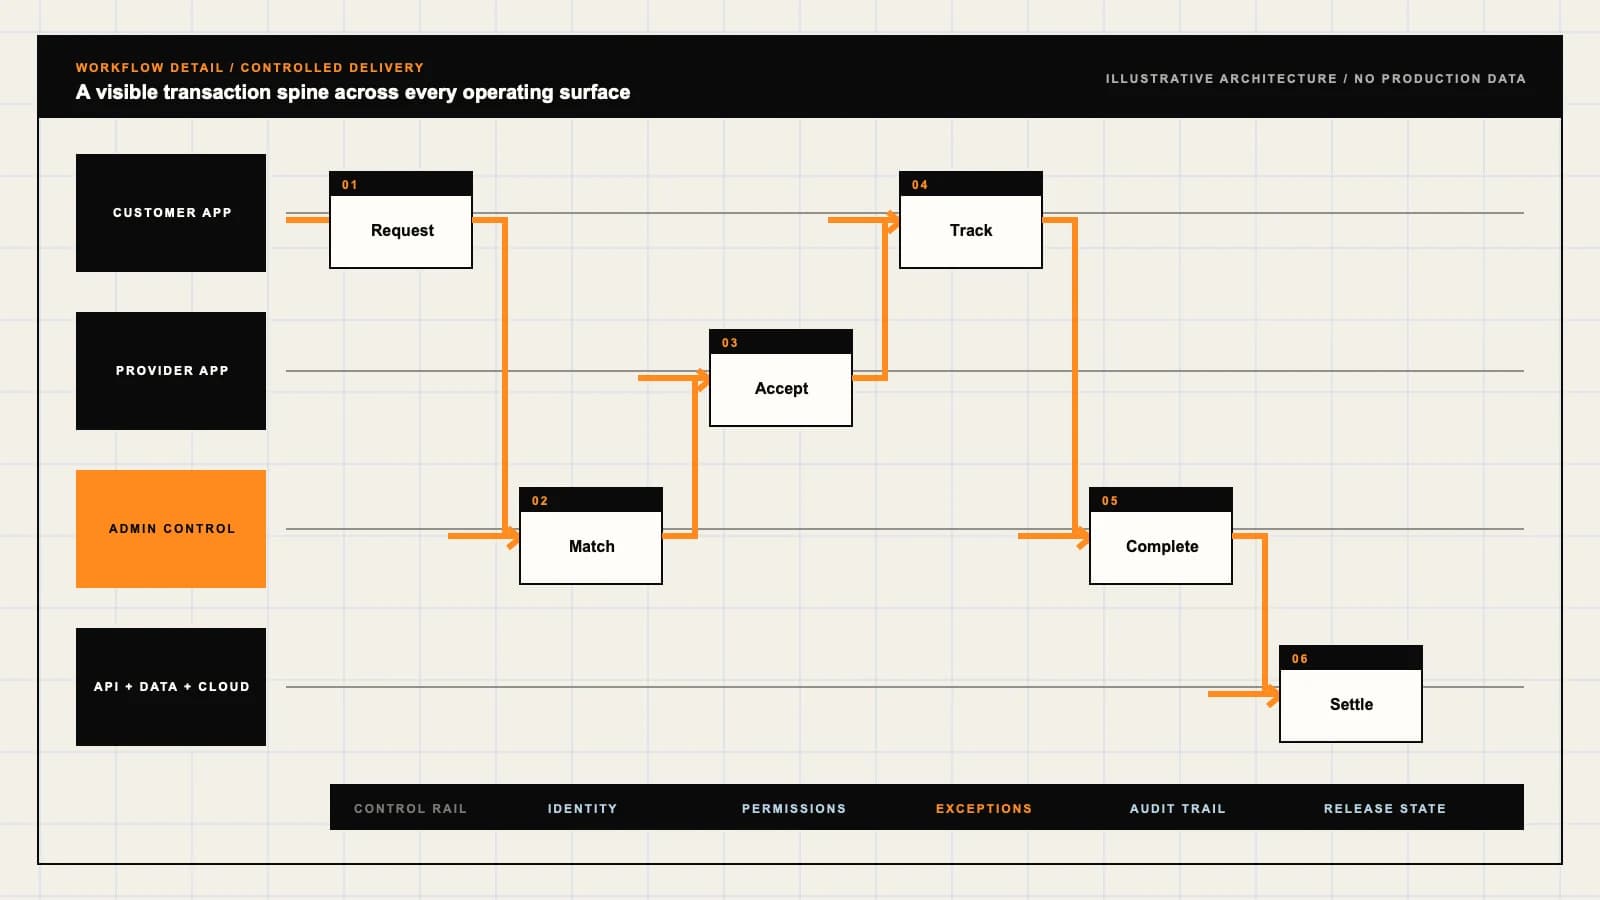
A committed upload bundle needs an inspectable manifest
Record the selected filenames, sizes and stable file identities in a transfer manifest. Distinguish choosing files, uploading parts, validating objects and committing the available bundle. A browser closing halfway should leave a recoverable upload or an explained failure; it must not publish an apparently complete package with missing content. Duplicate filenames need predictable archive names and visible mapping rather than one file quietly overwriting another.
Define what happens when a sender adds or removes a file before completion. Retry interrupted parts against the correct upload identity, then validate the committed result. A checksum can confirm the expected bytes under the chosen process; it does not establish that a file is safe or that the sender owns its rights. Rehearse a lost final response and return the existing transfer outcome without duplicating stored bundles or sending another notification.
Email delivery and link delivery create different evidence
The official WeTransfer notification guide distinguishes upload confirmation from download confirmation and describes different confirmation behavior for email and link transfers. It is a useful reference for naming events, not an assurance that another service can prove who read or retained the files.
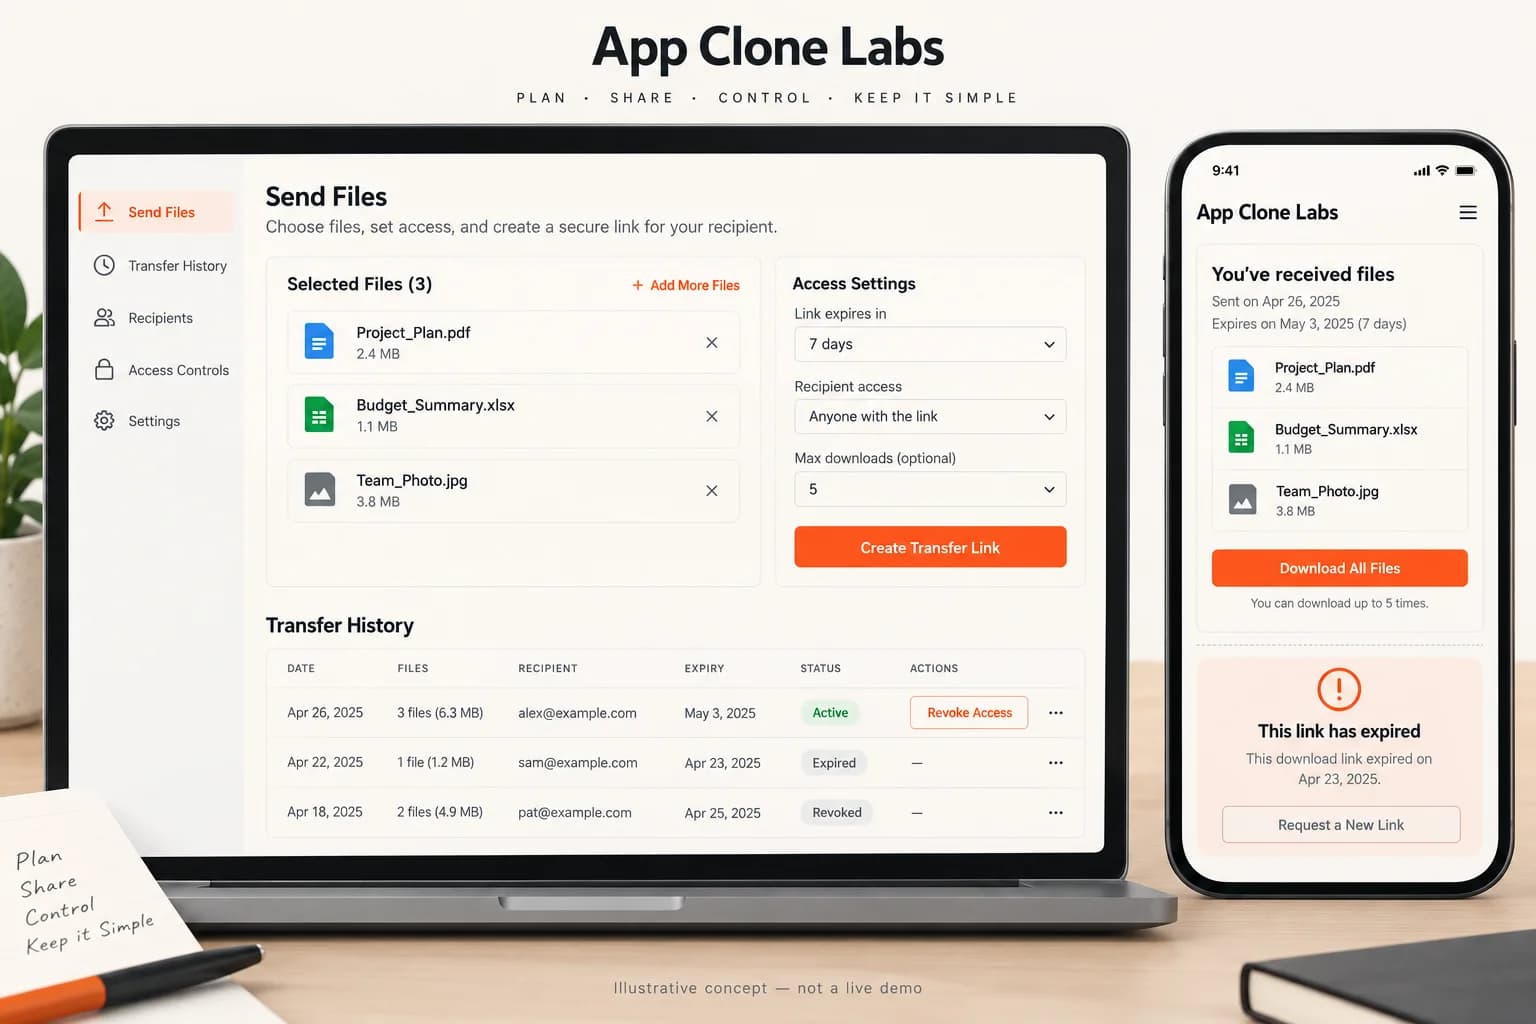
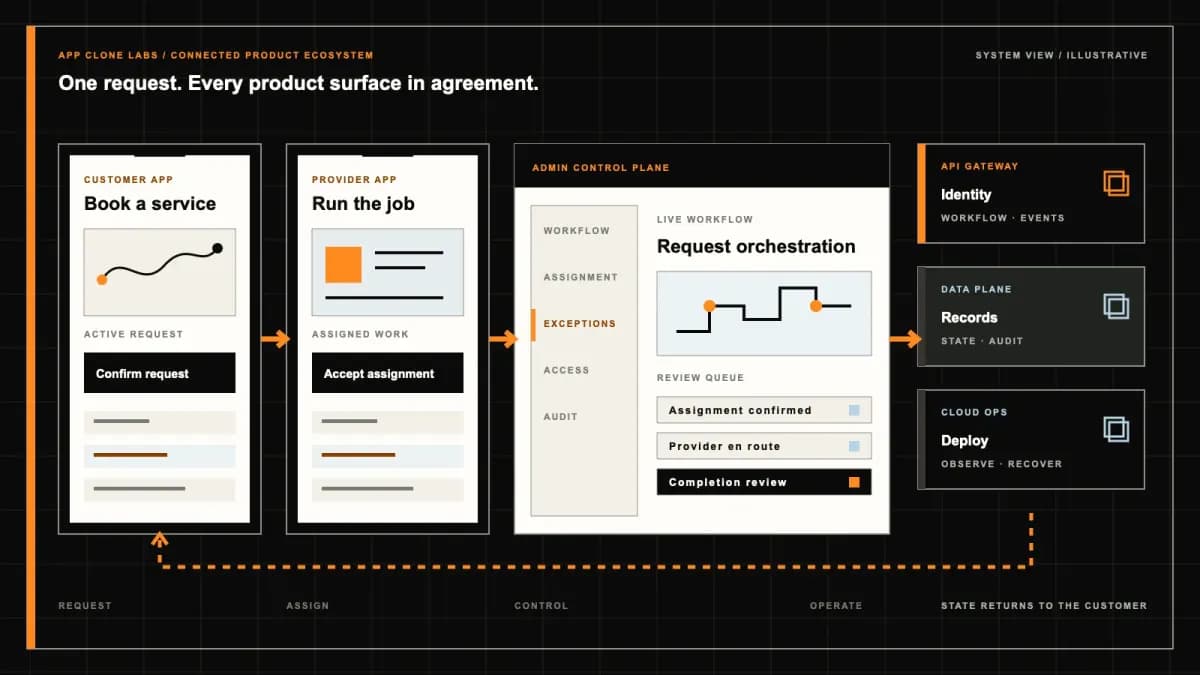
For an email transfer, show the reviewed recipients and the notice state separately from package readiness. Provider acceptance, a bounce, opening the landing page and completing a download are different observations. For a link transfer, the sender copies a link and distributes it independently. The service may have no reliable recipient identity. Define what your completion event measures, including individual-file downloads and archives, without turning an email address or automated preview request into proof of personal receipt.
Recipient mistakes need correction without exposing the address book
Ask the sender to review addresses before dispatch. Syntax validation can reject a malformed address but cannot prove a correctly formatted address belongs to the intended person. A typo can route a working link to someone else without causing a bounce. Explain the appropriate response: revoke the exposed transfer, review access records within their limits and create a replacement under the chosen policy.
Keep recipients private from other recipients unless a deliberate feature requires disclosure. Public transfer pages and notification previews should not reveal full addresses, sensitive subject lines or unrelated sender history. Limit saved-address suggestions and exports to authorized accounts. A resend should identify the chosen destination and preserve earlier outcomes, not silently notify everyone again. Test a bounce, an address corrected after sending and a forwarded notice, including the authority required to change or revoke the package.
A bearer link is access held by whoever possesses it
If possession of a link grants download access, say so plainly. Sending that link to one email address does not make the content exclusive to that recipient. Links can be forwarded, exposed in screenshots or processed by external preview services. Minimize visible metadata before access, avoid public indexing of transfer pages and restrict reusable delivery credentials in logs. A difficult-to-guess address is still a bearer link under this access model.
Passwords or verified-recipient checks create additional requirements for delivery, recovery and support. Agree those separately before describing a transfer as identity restricted. Keep sender management links distinct from recipient download links, with current authority checked before changes. Rehearse a copied link and a revoked sender session. Any encryption claims must match the actual storage, delivery and key-management design; a padlock graphic or HTTPS connection alone cannot establish every claimed protection.
Expiry and revocation stop supported access rather than recall copies
The official WeTransfer availability guide describes plan-dependent availability and conditional recovery after expiry. Those service terms belong to WeTransfer. Define the independent product’s expiry, retention and recovery contract instead of borrowing its durations or assuming that expired means immediately deleted.
Explain when expiry starts, which clock controls it and what a recipient sees after the deadline. Revocation is a sender or operator decision that may occur earlier. Recheck current eligibility when issuing new delivery access and define the effect on an already accepted stream. Expiry cannot erase files already downloaded onto another device. Separate public availability from storage deletion, backup retention and restricted evidence, with honest limits for recovery when the retained original is no longer available.
Partial archives and interrupted downloads need a visible retry route
A recipient requesting all files may wait while an archive is prepared. Show preparing, available and failed states without presenting an empty or truncated ZIP as a completed transfer. Preserve the committed manifest during archive generation, validate supported filename handling and define unsupported file conditions. If individual downloads are permitted, explain which files were selected and avoid claiming the full bundle arrived after only one item completed.
An interrupted network connection can leave a partial file on the recipient’s device. Explain supported resume or restart behavior and recheck link eligibility on a new request. Do not count a successful landing-page response as archive completion. Define the evidence available for server delivery and any client acknowledgement, including uncertainty when a browser closes. Test a failed archive, a download retry near expiry and a mobile device that runs out of local storage. Show the package size before download so the recipient can make a practical choice. A retry beginning after revocation should explain unavailable access rather than quietly redirecting to an old archive address that bypasses the current restriction.