
01Specify
Establish the project and allowed actions
Choose a template, supported stack, repository boundary, and acceptance examples before enabling generation.
White-label platforms
Branded prompt-to-product workspace with governed AI workflows. Planned for ai product companies, agencies, and enterprise innovation teams with role-specific workflows, operator controls, integrations, and a handover boundary defined for the selected market.
Professional plan. Enterprise customization is quoted on scope.
Custom workflows
Brand-safe product strategy
Admin and operations tooling
Reference walkthrough by arrangement
Workflow
Each workflow stage is mapped to a role, screen, API, notification, admin control, and measurable launch outcome.
Choose a template, supported stack, repository boundary, and acceptance examples before enabling generation.
Run a bounded job, record relevant inputs and provider usage, inspect the diff, and validate it in an isolated environment.
Separate preview from production, require the agreed approval, and retain the deployed revision and rollback reference.
Deployable Product Architecture
Workflow / system register
AI delivery loop
White-Label AI App Builder workflow stages.
Useful automation keeps judgment visible
Establish the project and allowed actions
Produce an attributable revision
Publish an explicitly reviewed output
Control note
Confidence, permissions, fallback behavior, and logs belong in the workflow.
Operator controls
The control center is scoped as a first-class product surface, not an afterthought.
Define runtime limits, network access, mounted files, package installation policy, and cleanup for generated code execution.
Scope repository and deployment tokens, redact logs, restrict provider access, and support revocation without editing generated files.
Reserve job budgets, expose consumed usage, stop uncontrolled retries, and explain cancelled, failed, or provider-limited jobs.
Integrations
External systems that determine launch readiness, data flow, and operational continuity.
Model providers with disclosed data handling, job limits, and version-aware evaluation
Repository adapters with scoped access, explicit branch targets, and attributable generated revisions
Isolated execution, preview hosting, deployment approval, billing meters, log redaction, and alerting
Scope drivers
The variables that most influence build effort, cost, and launch readiness.
A static prototype, database-backed app, and infrastructure-generating agent have very different permissions and validation burdens.
Supported stacks, package installation, network access, persistence, job duration, and concurrency determine sandbox requirements.
Define enterprise identity, provider routing, repository rights, retention, cost limits, and production approval before adding autonomy.
Deployable Product Architecture
Scope drivers / system register
AI delivery loop
White-Label AI App Builder scope drivers.
Useful automation keeps judgment visible
UI scaffolds versus full applications
Preview runtime and allowed tools
Teams, models, and data
Control note
Confidence, permissions, fallback behavior, and logs belong in the workflow.
V1 scope
Launch the smallest complete operating loop first, then scale the product with confidence.
Launch one declared stack with projects, membership, templates, prompts, revision history, and attributable files.
Let users inspect changes, see test results and errors, and restore a previous revision without silently losing work.
Expose quotas, provider failures, credential boundaries, support evidence, and an explicit preview-to-deployment gate.
Later phases
Capabilities that should usually wait until real usage proves the core loop.
Add required approvers, approved dependencies, template governance, and audit export once the initial path is reliable.
Compare supported providers against representative projects and failure cases rather than selecting by a marketing leaderboard.
Extend database migrations, test generation, and deployment targets only with corresponding permission and recovery controls.
Deployable Product Architecture
Later phases / system register
AI delivery loop
White-Label AI App Builder post-launch expansion.
Useful automation keeps judgment visible
Review policies and enterprise identity
Task-specific evaluation
Additional stacks and tools
Control note
Confidence, permissions, fallback behavior, and logs belong in the workflow.
Regulatory review
Each flag must be reviewed by qualified counsel for your target market before build or launch.
Reference walkthrough
Ask us to confirm which reference surfaces are currently available for this product model. Rather than publishing shared demo credentials, we schedule a private guided walkthrough for qualified buyers.
Request a role-specific demonstration and confirm which capabilities are currently available. Review the proposed responsibility: Create a project, describe the intended behaviour, inspect generated files and diffs, and decide what to keep.
Request a role-specific demonstration and confirm which capabilities are currently available. Review the proposed responsibility: Review code, dependencies, permissions, and tests; approve a known revision rather than an unbounded conversation.
Request a role-specific demonstration and confirm which capabilities are currently available. Review the proposed responsibility: Set member access, model credentials, spending limits, data retention, repository permissions, and deployment authority.
Request a live, private walkthrough of the reference implementation. We will confirm scope and discuss configured deployment versus custom build for your market.
Open registerDeployable Product Architecture
Reference walkthrough / system register
AI delivery loop
Request a White-Label AI App Builder reference walkthrough.
Useful automation keeps judgment visible
Builder: Turn a brief into reviewable changes
Reviewer: Check the result before promotion
Workspace owner: Govern providers and execution
Book a walkthrough
Control note
Confidence, permissions, fallback behavior, and logs belong in the workflow.
User roles
Clone-inspired platforms usually need several coordinated interfaces, not just a customer app.
Create a project, describe the intended behaviour, inspect generated files and diffs, and decide what to keep.
Review code, dependencies, permissions, and tests; approve a known revision rather than an unbounded conversation.
Set member access, model credentials, spending limits, data retention, repository permissions, and deployment authority.
Live demo
Open each app or panel in a new tab and sign in with the demo login shown. The demos run on shared sample data, carry our demo product names, and show the ready-made product before any customization.
Free Workspace
demo@mxbolt.com | demo1234Pro Tier
pro@mxbolt.com | pro1234Enterprise Tier
enterprise@mxbolt.com | ent1234Operator Admin
admin@mxbolt.com | admin1234Bring a representative app requirement, supported stack and team roles to a guided walkthrough. Use this control-panel reference to discuss provider, repository and deployment boundaries, then ask to follow a generation job through review, export and recovery. Confirm the current demo and supported scope before choosing the build.
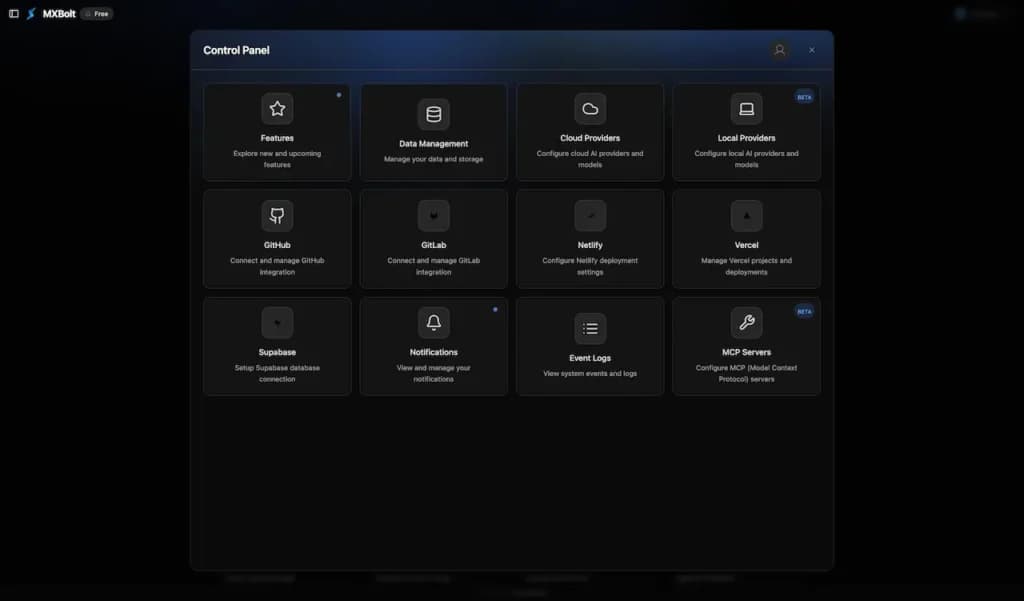
Control-panel reference with MXBolt demo branding. Provider, repository, hosting and data-service names identify scope candidates, not verified connections or included services. This screen does not demonstrate AI generation, source export, access enforcement or deployment.
What to check in the walkthrough
Product flow
A visual map of how each role interacts with each workflow stage, with operator controls and integration boundaries.
Deployable product architecture
White-Label AI App Builder
Workflow
Roles in the loop
Operator controls
Integrations underneath
Monetization
We model monetization early so payments, admin controls, and reporting support the business.
Define included members, active projects, storage, preview environments, and support access per plan.
Specify how tokens, jobs, retries, and tool execution affect billing; explain rounding and disputed usage.
Scope private routing, approved templates, audit exports, retention policy, and operational support without implying a certification.
Artifact register
Reference screens illustrate workflows, not a contracted feature list. Sample prices, data, and responses are demonstration content; confirm the current scope during a walkthrough.
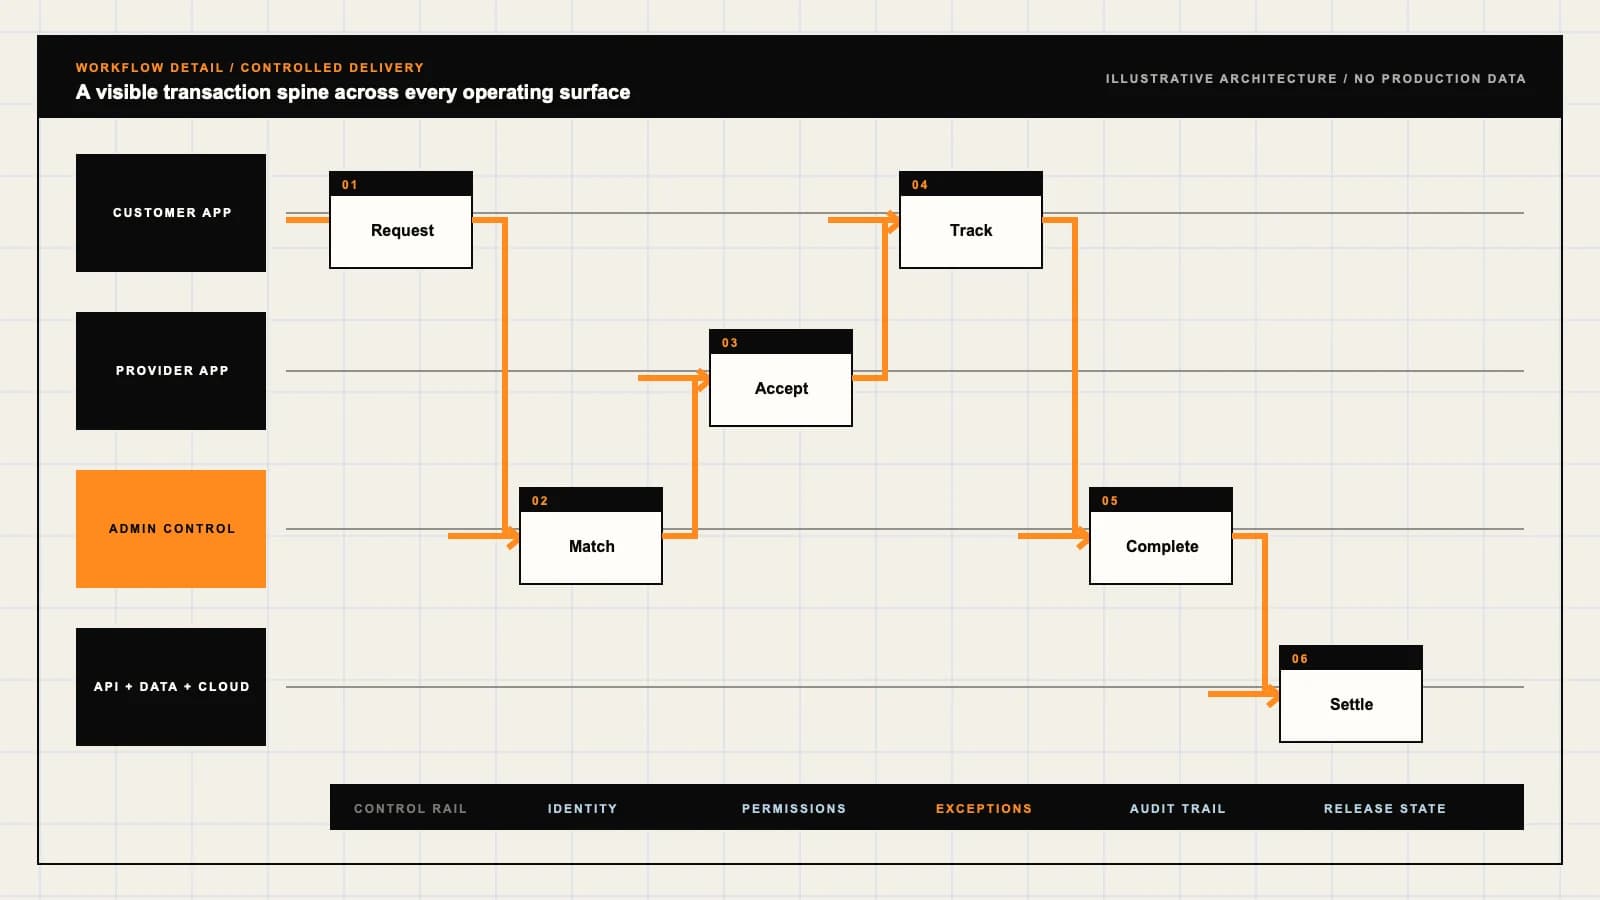
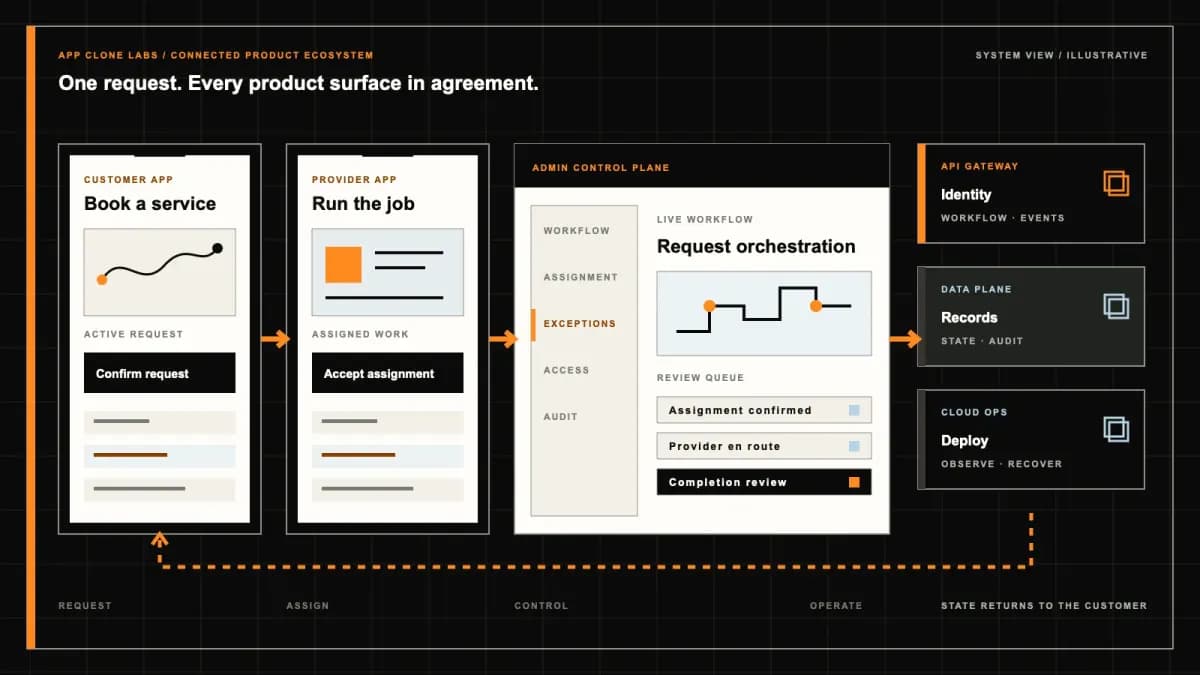
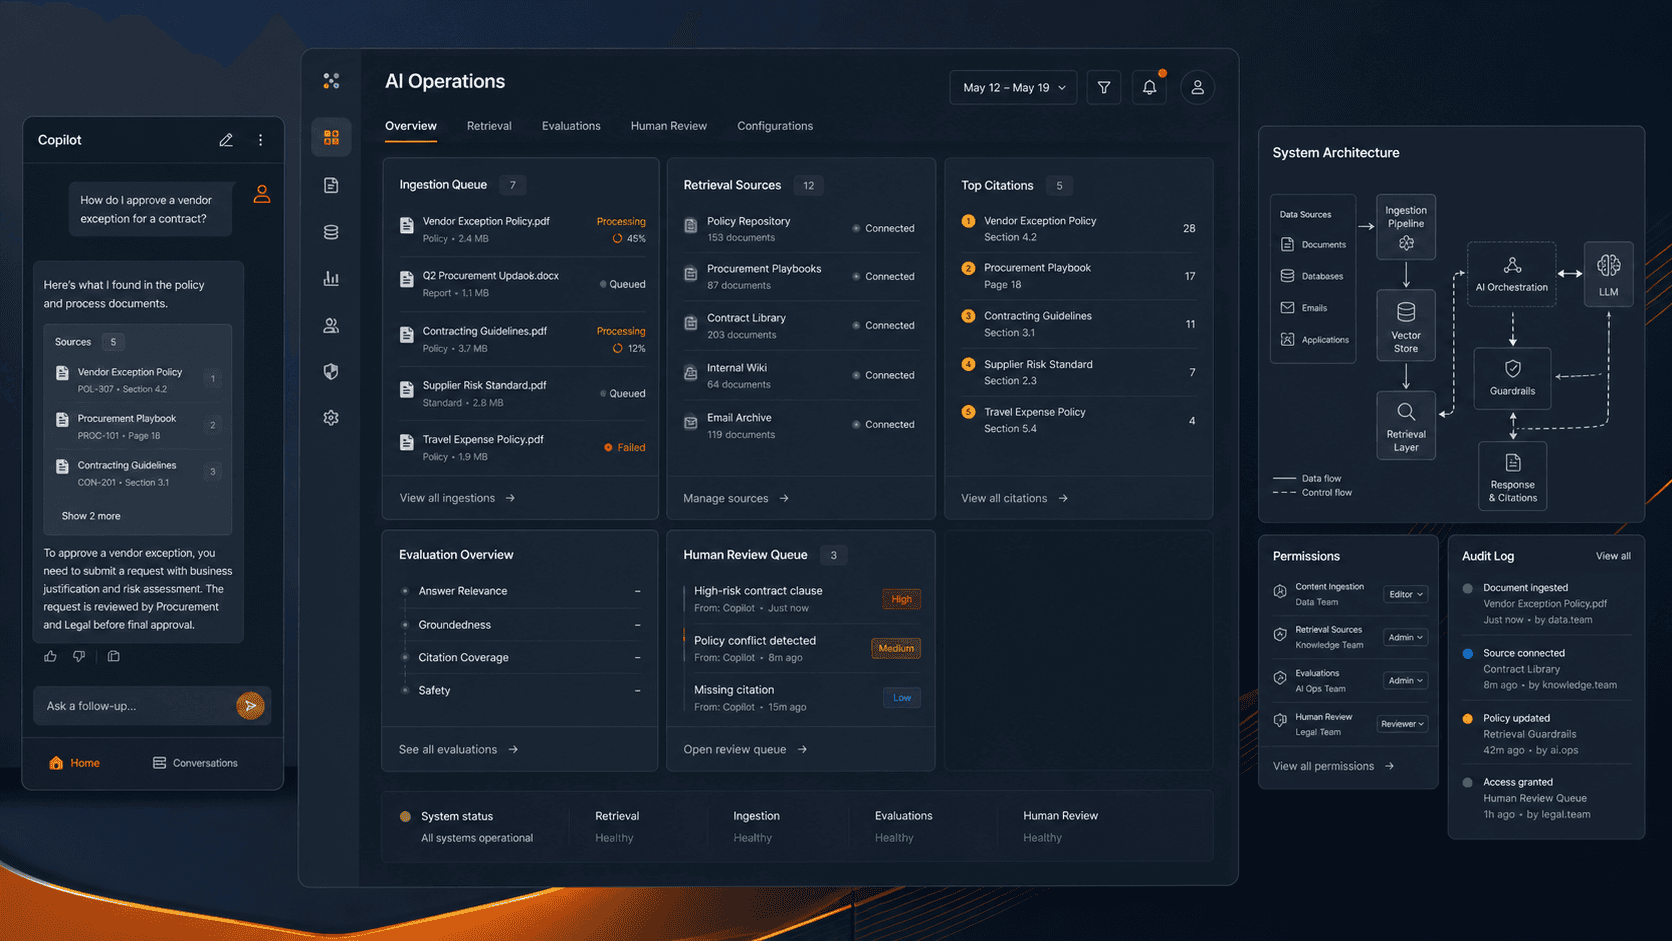
A user asks for a booking screen with a database and an admin login. An AI model returns plausible code. The important questions start there: which files changed, which packages were installed, where the code will run, whether it exposed a credential, and whether the user can restore the previous working version. A white-label AI app builder needs an accountable project workflow around generation, not just a chat box carrying your logo.
App Clone Labs can scope a branded builder workspace with projects, generation jobs, artefact history, previews, usage controls, and agreed publishing integrations. The initial product should declare exactly what it can produce: interface prototypes, a supported application stack, or more extensive code changes. A working preview is not evidence that generated code is secure, accessible, maintainable, or production-ready.
A frontend scaffold has a smaller operating boundary than a system that creates databases, installs dependencies, and changes cloud resources. Select a stack and project template that the team can test and support. Define which folders the agent can edit, which commands it can run, and which services it may contact. Unsupported requests should return an explanation rather than silently improvising infrastructure.
Turn a customer brief into acceptance examples before generation. For a booking screen, those might include a required date, a duplicate submission, an unavailable slot, keyboard navigation, and an authorised admin view. Store the brief and test expectations with the project revision. This makes later review about the requested behaviour rather than whether the generated page happens to look convincing.
The workspace owns projects and member permissions. Each generation request creates a job with a bounded input and an observable outcome. A successful job produces a revision or proposed diff; it should not overwrite the only usable project state. Failed, cancelled, and provider-limited jobs need distinct outcomes so a user knows whether files changed and whether another attempt is appropriate.
Record the model and relevant configuration, input references, generated changes, tool actions, and validation outcome under the agreed retention policy. Avoid collecting raw private prompts indefinitely simply because they may help troubleshooting. When a project is deleted, define what happens to files, previews, provider submissions, logs, and billing records; they may have different permitted retention periods.
A repository comment, uploaded specification, or model response can contain instructions that conflict with the owner’s policy. The builder must not grant new permissions because text asks for them. Enforce file, tool, network, and deployment boundaries outside the model. A reviewer should see attempts to use a forbidden command or destination as a policy event, not just a mysterious generation failure.
The OWASP LLM application security project describes risks including prompt injection and excessive agency. Those references inform a threat model; they do not certify this product or establish that a particular model cannot be manipulated.
For code execution, specify a sandbox with job time limits, resource limits, controlled network access, and a clear cleanup rule. Do not share a writable project directory across unrelated tenants. Prevent a generated application from reading the builder service’s own environment or credentials. Preview assets, logs, and downloadable archives require the same project-level authorisation as the editor.
A repository connection should identify the installation, repositories, branch targets, and permitted actions. Where possible, create a reviewable change rather than modifying a protected branch. Record who approved the publication and which revision was sent. Disconnecting the integration must remove effective access, not merely hide a connected badge in the interface.
For workflows that use GitHub automation, GitHub’s secure-use guidance provides permission and secret-handling considerations. Repository access should be scoped to the required action, and deployment credentials should not be embedded in generated source or model prompts.
Preview and production need separate credentials and approval rules. A user should know whether a publish action creates a temporary preview or changes a live application. Preserve the deployed revision, environment configuration reference, and rollback path. Database-changing code requires a migration and recovery review; reverting application files alone may not reverse its effect on data.
A subscription can include workspace seats and project limits, while generation may consume variable provider and execution resources. Define the billable unit, included allowance, reservation behaviour, retry treatment, and cancellation treatment before building the credit screen. The customer should be able to connect a charge to a job without seeing another tenant’s prompt or provider credential.
Reserve capacity before a job starts and release unused allowance according to policy. Bound automatic retries so a failing provider cannot drain a budget in the background. Give workspace owners spending limits and useful alerts. Useful product measures include generation success, review acceptance, test pass rate, latency distributions, and usage per accepted revision. Compare those measures against representative briefs and agreed project limits.
Ask to see the original brief, generated diff, test output, preview, and a requested correction. Then try a failing dependency, an interrupted job, a forbidden file access, and a restore action. Confirm what happens when the provider is unavailable or a spending limit is reached. The control-panel reference shown here illustrates possible entry points; it does not verify active repositories, providers, or production deployment connections.
If your goal is an application rather than selling an application builder, SaaS development may be the more direct route. A builder adds a product layer for generation, review, usage, and safe execution; that additional layer should have a clear audience and operating owner.
Bring representative user briefs, supported stacks, expected repository actions, desired preview environments, provider preferences, data-handling requirements, and billing rules to discovery. The proposal should specify which artefacts clients can export, the applicable code and dependency licences, the operator’s access, and which components remain third-party services. Generated output does not establish unrestricted intellectual-property rights by itself.
Acceptance needs representative tasks and deliberately failing cases, not a single successful prompt. Define who reviews security, accessibility, dependency changes, and deployment readiness. Add new frameworks, private model routing, or more autonomous tools only when their permissions and recovery paths can be evaluated. The useful promise is an inspectable, governed workflow with stated limits—not instant production software from every request.
FAQ
The intended product is a governed project workspace around generation: supported templates, jobs, revisions, previews, review, usage, and publishing controls. A conversational interface is one part of that workflow, not the complete platform.
The supported stack must be agreed and tested. Begin with a narrow template and known dependencies; additional frameworks require their own runtime, validation, and support boundaries.
Only within an explicitly agreed permission model. Preview and production should be separate, with known revisions, scoped credentials, appropriate review, and a rollback path. Generation success alone is not production approval.
Define workspace authorisation, provider data handling, retention, secret redaction, scoped integration tokens, and access revocation. Enforce permissions outside the model and test cross-project access.
No. Generated code requires tests and appropriate human review. Evaluate representative tasks and failure cases; a preview or model response does not establish security, correctness, or licensing compliance.
This can be scoped with credential isolation, allowed models, usage limits, disclosed data handling, and failure behaviour. A listed provider is a candidate integration until the actual connection is tested.
Define billable units, reserved allowance, retry limits, cancellation treatment, and provider failure rules. Show usage against identifiable jobs and prevent uncontrolled retries from consuming an entire workspace budget.
Test a brief, revision diff, correction, preview, restore, failed dependency, provider outage, and forbidden tool action. Also inspect permissions, usage records, and the distinction between preview and production publishing.
Solution reference register
01 / Regulatory caveat
AI use, privacy, copyright, and data-processing review required · Generated code and content require human review before production use · Model provider terms and retention policies must be disclosed per tenant
Primary sources
Dated official documentation, standards, and research that support the factual claims on this page.
How to read this page
Scope, cost and timeline figures are planning guidance until confirmed in a written proposal. Diagrams and screens are illustrations, not client deliverables, and source-code rights and handover follow the signed agreement. See the delivery process and the full disclaimer.