01Join
Create or accept a conversation within a tenant
Resolve identity, membership, channel policy, blocked contacts, consent, and the allowed message types before a composer can submit content.
White-label platforms
Branded real-time messaging and collaboration platform. Planned for communities, service businesses, and teams launching private communication products with role-specific workflows, operator controls, integrations, and a handover boundary defined for the selected market.
Professional plan. Enterprise customization is quoted on scope.
Custom workflows
Brand-safe product strategy
Admin and operations tooling
Reference walkthrough by arrangement
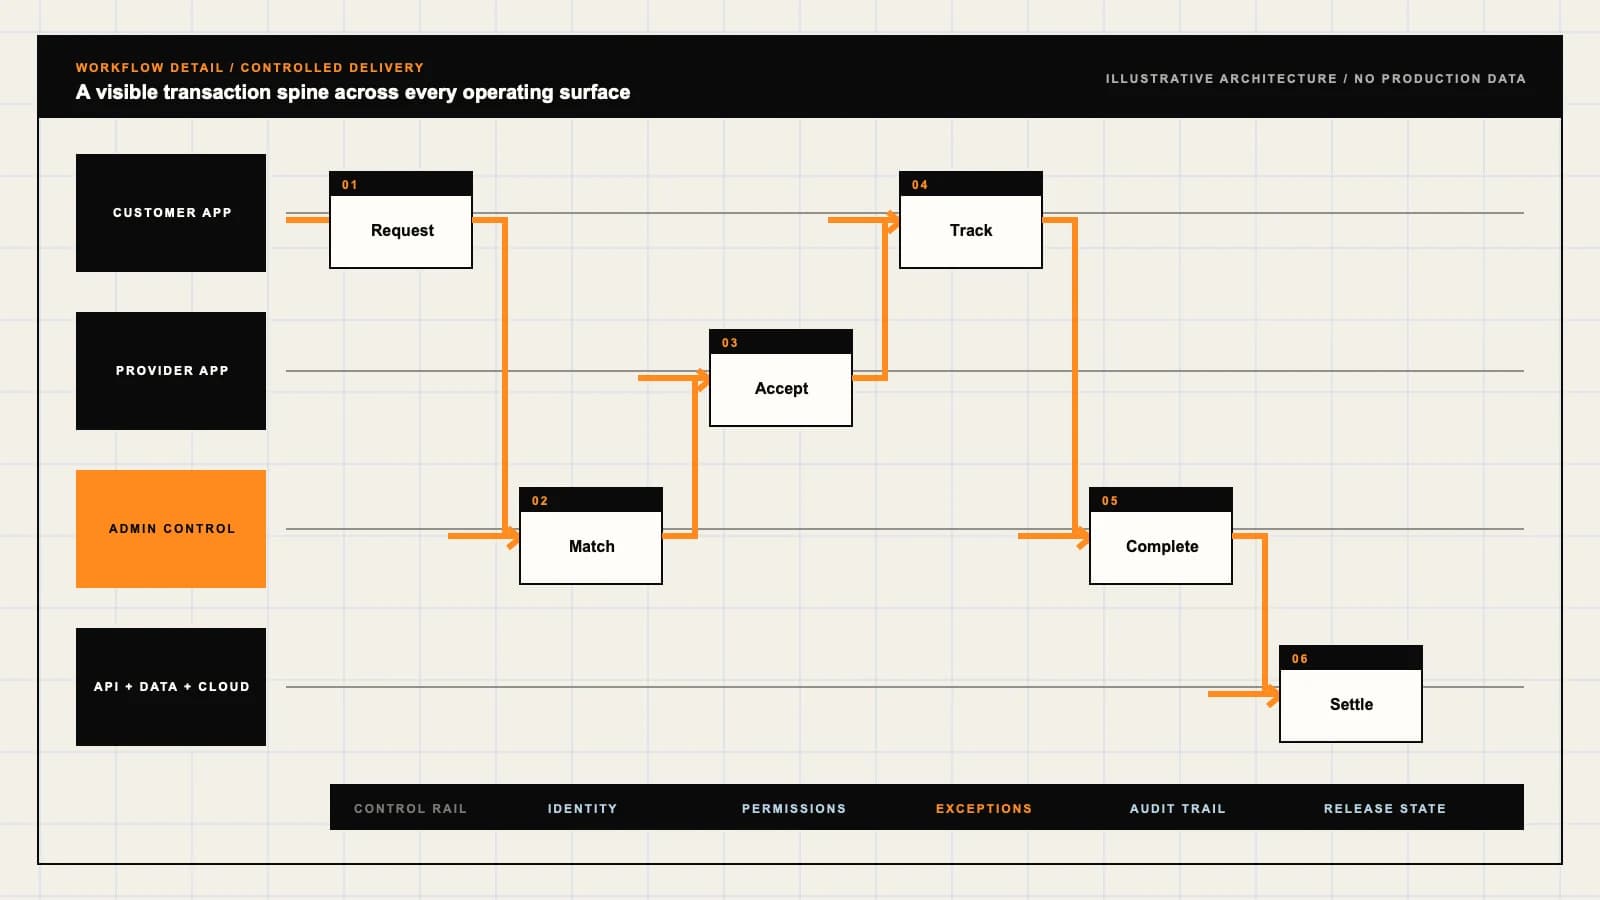
Workflow
Each workflow stage is mapped to a role, screen, API, notification, admin control, and measurable launch outcome.
Resolve identity, membership, channel policy, blocked contacts, consent, and the allowed message types before a composer can submit content.
Persist an idempotent message event, fan it out to permitted devices, and distinguish accepted, delivered, read, failed, edited, and deleted states.
Route a report or delivery exception to the right role, apply a documented action, and restore service or data from a tested recovery path.
Deployable Product Architecture
Workflow / system register
Product delivery loop
White-Label Messaging App workflow stages.
A focused release proves one complete workflow
Create or accept a conversation within a tenant
Track message lifecycle honestly
Handle reports, retention, and recovery
Control note
Scope the customer action and the operator response as one system.
Operator controls
The control center is scoped as a first-class product surface, not an afterthought.
Enforce tenant and membership checks on APIs, search, media, notifications, exports, support tools, caches, queues, and backups.
Separate member visibility from moderator evidence access, record reason codes, and make urgent account or content actions reversible where policy allows.
Version retention schedules, deletion requests, export authority, key ownership, and legal-review steps instead of promising universal deletion or secrecy.
Integrations
External systems that determine launch readiness, data flow, and operational continuity.
Identity, session management, device registration, push notifications, and optional single sign-on with tenant-scoped roles
Object storage, malware scanning, search indexing, observability, and a queue or realtime transport selected for the message volume and recovery target
Billing, support, moderation case management, export tooling, and backup storage with provider events and retention settings documented
Scope drivers
The variables that most influence build effort, cost, and launch readiness.
Each model changes membership rules, unread counts, mention behaviour, moderation authority, and notification defaults.
Define what accepted, delivered, read, failed, and retried mean; a push acknowledgement is not proof that a person saw a message.
Retention duration, legal holds, tenant exports, backups, and encryption-key ownership determine storage design and support procedures.
Deployable Product Architecture
Scope drivers / system register
Product delivery loop
White-Label Messaging App scope drivers.
A focused release proves one complete workflow
Direct, group, channel, or business inbox
Best-effort, durable, or regulated workflow
History, media, export, and deletion
Control note
Scope the customer action and the operator response as one system.
V1 scope
Launch the smallest complete operating loop first, then scale the product with confidence.
Deliver text and agreed attachments, preserve ordering metadata, support edit or delete policy, and show reliable unread and failure states.
Give moderators the minimum evidence needed for a decision while preserving member privacy and attributable actions.
Configure a bounded tenant, test cross-tenant denial, export approved records, and restore a non-production backup before handover.
Later phases
Capabilities that should usually wait until real usage proves the core loop.
Add routing, working hours, templates, and SLA reporting only after the member-versus-agent visibility model is explicit.
Extend residency or key ownership after reviewing provider capabilities, recovery responsibilities, lawful-access procedures, and operational failure modes.
Introduce rules or classifiers with human review, explainable outcomes, rate limits, and a safe fallback when a model or provider fails.
Deployable Product Architecture
Later phases / system register
Product delivery loop
White-Label Messaging App post-launch expansion.
A focused release proves one complete workflow
Assignment and service workflows
Regional storage or client-managed keys
Notifications and moderation assistance
Control note
Scope the customer action and the operator response as one system.
Regulatory review
Each flag must be reviewed by qualified counsel for your target market before build or launch.
Reference walkthrough
Ask us to confirm which reference surfaces are currently available for this product model. Rather than publishing shared demo credentials, we schedule a private guided walkthrough for qualified buyers.
Request a role-specific demonstration and confirm which capabilities are currently available. Review the proposed responsibility: Find permitted people or channels, send a message, see its delivery state, manage notifications, and recover access without exposing another tenant’s data.
Request a role-specific demonstration and confirm which capabilities are currently available. Review the proposed responsibility: Process abuse reports, apply the approved action, preserve relevant evidence, and escalate urgent cases using scoped access and an audit trail.
Request a role-specific demonstration and confirm which capabilities are currently available. Review the proposed responsibility: Configure membership, retention, export, notification, and support policies while separating tenant administration from platform-wide security duties.
Request a live, private walkthrough of the reference implementation. We will confirm scope and discuss configured deployment versus custom build for your market.
Open registerDeployable Product Architecture
Reference walkthrough / system register
Product delivery loop
Request a White-Label Messaging App reference walkthrough.
A focused release proves one complete workflow
Member: Start and understand a conversation
Moderator: Review reports without becoming a reader of everything
Tenant owner: Operate a branded communication service
Book a walkthrough
Control note
Scope the customer action and the operator response as one system.
User roles
Clone-inspired platforms usually need several coordinated interfaces, not just a customer app.
Find permitted people or channels, send a message, see its delivery state, manage notifications, and recover access without exposing another tenant’s data.
Process abuse reports, apply the approved action, preserve relevant evidence, and escalate urgent cases using scoped access and an audit trail.
Configure membership, retention, export, notification, and support policies while separating tenant administration from platform-wide security duties.
Live demo
Open each app or panel in a new tab and sign in with the demo login shown. The demos run on shared sample data, carry our demo product names, and show the ready-made product before any customization.
First Account
+919876543210 | 123456Second Account
+911234567890 | 123456Admin Side
Android Build
Use these two messaging references to plan how members find conversations, manage preferences and participate in groups. Bring your moderation, privacy and retention requirements to a guided walkthrough, and ask to test tenant boundaries with sample accounts. Confirm the current demo and supported scope before choosing the build.
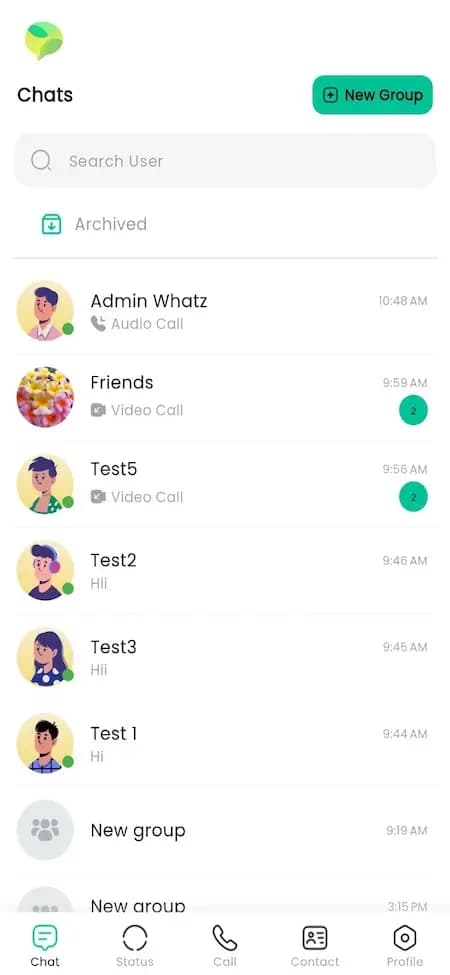
Conversation-list reference with source demo branding, sample accounts and avatars. The branding is reference context, not an affiliation or client endorsement. Group entries and call previews do not establish moderation, message delivery, encryption or functioning calls.
What to check in the walkthrough
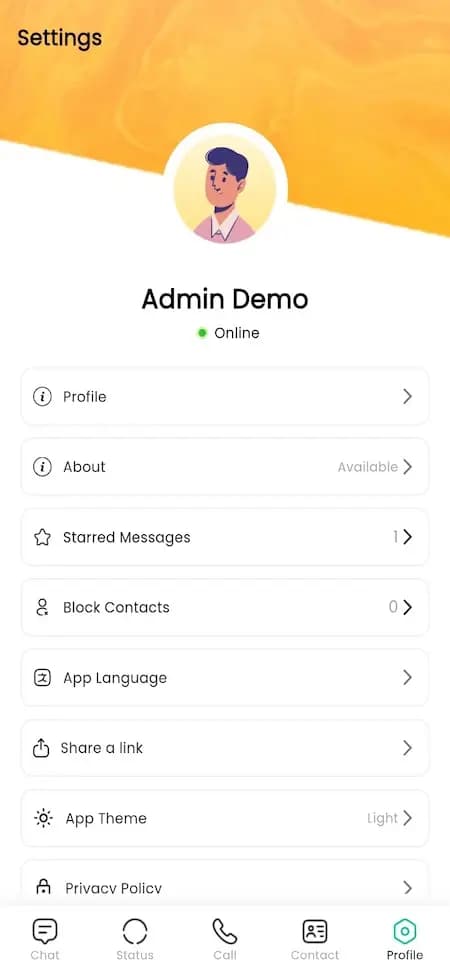
Member-settings reference with a sample profile labelled Admin Demo. The name does not establish an administrator console or permissions. Source branding and sample content are reference context, not affiliation or client proof; visible settings and a privacy-policy link do not verify privacy controls.
What to check in the walkthrough
Product flow
A visual map of how each role interacts with each workflow stage, with operator controls and integration boundaries.
Deployable product architecture
White-Label Messaging App
Workflow
Roles in the loop
Operator controls
Integrations underneath
Monetization
We model monetization early so payments, admin controls, and reporting support the business.
Charge for configured tenants, member limits, support boundaries, and agreed operating responsibility rather than promising a universal feature set.
Define quotas, overage treatment, media limits, and deletion behaviour clearly before a tenant upgrades.
Scope human review, response windows, escalation, and evidence handling separately from the software subscription.
Artifact register
Reference screens illustrate workflows, not a contracted feature list. Sample prices, data, and responses are demonstration content; confirm the current scope during a walkthrough.
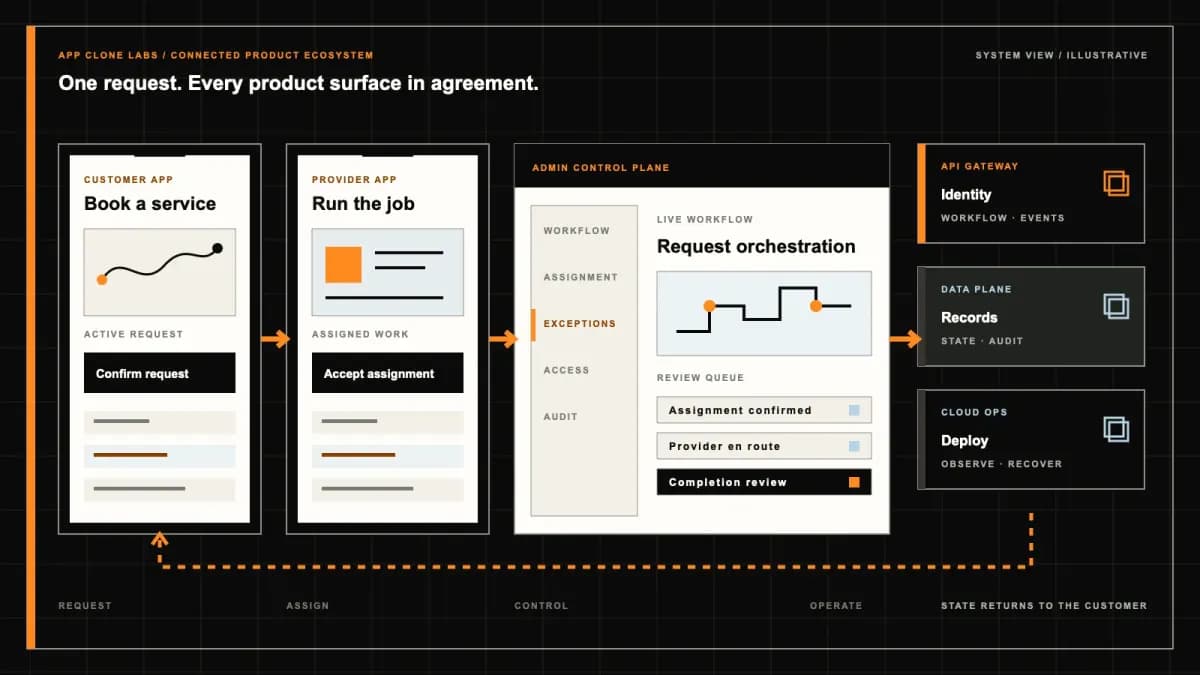
A white-label messaging app is not only a chat screen with a different logo. It is a branded communication service with tenant boundaries, identity, conversation membership, message persistence, notification decisions, moderation, retention, and support recovery. App Clone Labs can help translate your approved operating model into an original product, but the scope must define what a message state means, who may inspect content, how long records remain, and what happens when a device, provider, or account fails. The reference screen on this page illustrates settings direction; it does not prove encryption, delivery, or audited privacy controls.
Decide whether the first release supports direct messages, private groups, public channels, agent inboxes, or a deliberate subset. A conversation needs an owner or tenant, participants, membership events, policy, and a lifecycle. Invitations can be pending, accepted, declined, expired, or revoked. A blocked contact may still appear in an existing record while new delivery is prevented. A removed member may retain access to their permitted history or may lose it under a defined policy. These decisions affect database constraints, notification jobs, search indexes, exports, and moderation evidence. Copying a familiar chat layout does not resolve them.
Persist an idempotent message identifier, author, conversation, creation time, content version, attachment references, and policy state. Then represent lifecycle events such as accepted, queued, delivered to a device, read by an account, edited, retracted, or failed. “Sent” normally means the service accepted a request; it does not necessarily mean a recipient device received it. “Read” should be tied to a documented account or device signal, not inferred from a push provider callback. If a sender needs a stronger business acknowledgement, model that as a separate action instead of relabelling a transport event.
Realtime transport can disconnect, push providers can delay or reject notifications, and a device can remain offline. Use an outbox or equivalent durable handoff so a retry does not create duplicate messages. Store provider event identifiers and make handlers idempotent. Show a member whether a message is pending, delivered, failed, or awaiting retry, and give support a traceable reference. A green check icon is not evidence that every recipient saw content. Define ordering for reconnects and edits, and test simultaneous sends from multiple devices.
For the transport and API boundary, compare the custom web and mobile app development approach with the actual devices, tenancy, and recovery targets in your brief. A realtime library can move bytes; it does not define authorization, retention, or support policy.
A tenant boundary must hold on every path that can reveal a conversation. Check message APIs, unread counters, search, attachment URLs, notification payloads, analytics, support impersonation, exports, caches, background queues, logs, and backups. A shared database can be viable with carefully enforced tenant and membership predicates, but a support dashboard should not use a broad service credential that bypasses them. Test a member attempting to access another tenant’s conversation, attachment, notification preview, and export. Record the denial as a regression case, not a one-time manual check.
Members need report, block, mute, and appeal paths. Moderators need enough evidence to apply the tenant policy, but their access should be scoped by role, case, time, and reason. Store report status, reason code, reporter, subject, action, reviewer, and escalation outcome. Decide whether an attachment is quarantined, whether a conversation is temporarily restricted, and how an accused member is notified. Preserve an audit record without placing raw message text into every operational log. For urgent threats, define the human escalation and account-protection procedure outside the composer itself.
Do not promise end-to-end encryption merely because traffic uses TLS or data is encrypted at rest. End-to-end designs change search, moderation, multi-device recovery, backups, key rotation, and lawful-access handling. If the service can inspect content for moderation or server-side search, describe that boundary accurately. If a tenant brings its own keys, document who can recover data when a key is lost and which support actions become impossible. The proposal should name the threat model, key custody, device verification, metadata exposure, and recovery responsibilities; the software page should not imply a security certification that has not been independently assessed.
The Messaging Layer Security RFC 9420 describes a protocol family for group messaging. It is a technical reference, not proof that an implementation is secure, compliant, or appropriate for your threat model. Select and review any protocol with qualified security specialists.
Notification previews can expose message content on a shared lock screen. Let each tenant and member choose preview, sound, badge, mention, quiet-hour, and device settings within platform limits. Keep notification payloads minimal and treat push delivery as a hint to sync, not as the message store. A muted conversation should not silently reappear because another device registered. Define how a revoked device, logged-out session, or deleted account affects tokens and queued notifications. Marketing notifications need a different consent and unsubscribe path from essential service alerts.
Write the retention policy before adding an “auto-delete” toggle. Specify message history, attachments, reports, audit records, search indexes, notification logs, backups, and legal holds separately. A deletion request may remove a member’s content from active views while an immutable audit or approved legal hold remains. Explain that backups have a restoration window and may not disappear immediately. Exports should be authorized, scoped, encrypted in transit, and logged; an export link must not become a permanent copy with no expiry. Recovery drills should confirm which records return and which policy state is re-applied.
A sensible first release might include one tenant model, direct and small-group text messages, agreed attachments, device registration, read-state semantics, report and block flows, scoped moderator access, push notifications, retention settings, export, and a tested backup restore. Leave business inbox routing, large public channels, client-managed keys, automated moderation, multi-region residency, and complex message search for later unless the operating evidence is ready. A smaller state machine that support can explain is more valuable than a long feature list that cannot distinguish accepted from delivered.
For a familiar reference category, the WhatsApp-style messaging product brief can help frame direct and group conversation expectations. It does not grant another company’s code, brand, protocol choices, encryption claims, or commercial results; your app needs its own requirements and evidence.
Bring your tenant model, message types, notification policy, retention schedule, moderation rules, export format, provider assumptions, and recovery objective to discovery. Request a walkthrough that includes an invitation, a blocked member, a duplicate provider event, an offline device, a failed attachment, a report with limited moderator access, an expired retention record, and a restored backup. Ask which screens are illustrative and which integrations are actually connected. The agreement should define source-code ownership, third-party terms, hosting, support, security review, acceptance evidence, and maintenance. A branded messaging interface can be a strong product foundation when its promises match its controls.
FAQ
No. A familiar product can clarify category expectations, but the delivered application should use original branding, design, code, workflows, and policies. Third-party source code, protected assets, protocol claims, and commercial outcomes are not implied.
Delivered should identify the agreed device or account acknowledgement. Read should identify a documented user or account signal. A push callback or a green send icon alone does not prove that a person saw the message.
Yes, if tenant scope is defined across identity, conversations, media, search, notifications, support, exports, queues, logs, and backups. Branding alone is not isolation.
Encryption depends on the selected architecture and threat model. TLS and encryption at rest do not by themselves provide end-to-end encryption. Key custody, moderation, search, multi-device recovery, and legal-access boundaries require explicit review.
Use a scoped case workflow with reason codes, minimum necessary evidence, reviewer attribution, escalation, and retention rules. Moderation access should not automatically grant unrestricted access to every tenant conversation.
Not necessarily. Active data, indexes, reports, audit records, legal holds, and backups have different lifecycles. The policy should disclose restoration windows and how deletion is applied to each copy.
No. Push services can delay, reject, or suppress notifications. The durable message store and sync process should determine message availability; notification events are signals rather than proof of receipt.
Confirm demo availability separately, then test tenant denial, membership changes, duplicate events, offline recovery, report handling, retention, export authorization, and backup restore with non-production records. Reference screens alone do not prove an operating integration.
Solution reference register
01 / Regulatory caveat
Privacy, retention, lawful access, and abuse-response review required · Encryption and key-management responsibilities must be documented · User reporting, blocking, and account recovery paths must be tested
Primary sources
Dated official documentation, standards, and research that support the factual claims on this page.
How to read this page
Scope, cost and timeline figures are planning guidance until confirmed in a written proposal. Diagrams and screens are illustrations, not client deliverables, and source-code rights and handover follow the signed agreement. See the delivery process and the full disclaimer.