An operator pauses shopping after a faulty release, but a customer already has an active ride and a pending shopping refund. Disabling the whole account would abandon the ride; hiding the shopping tile would not settle the refund. A multi-service platform needs distinct transaction owners, permission boundaries and safe restriction controls. The meaningful product question is what remains accessible when one service fails, not how many services fit on the home screen.
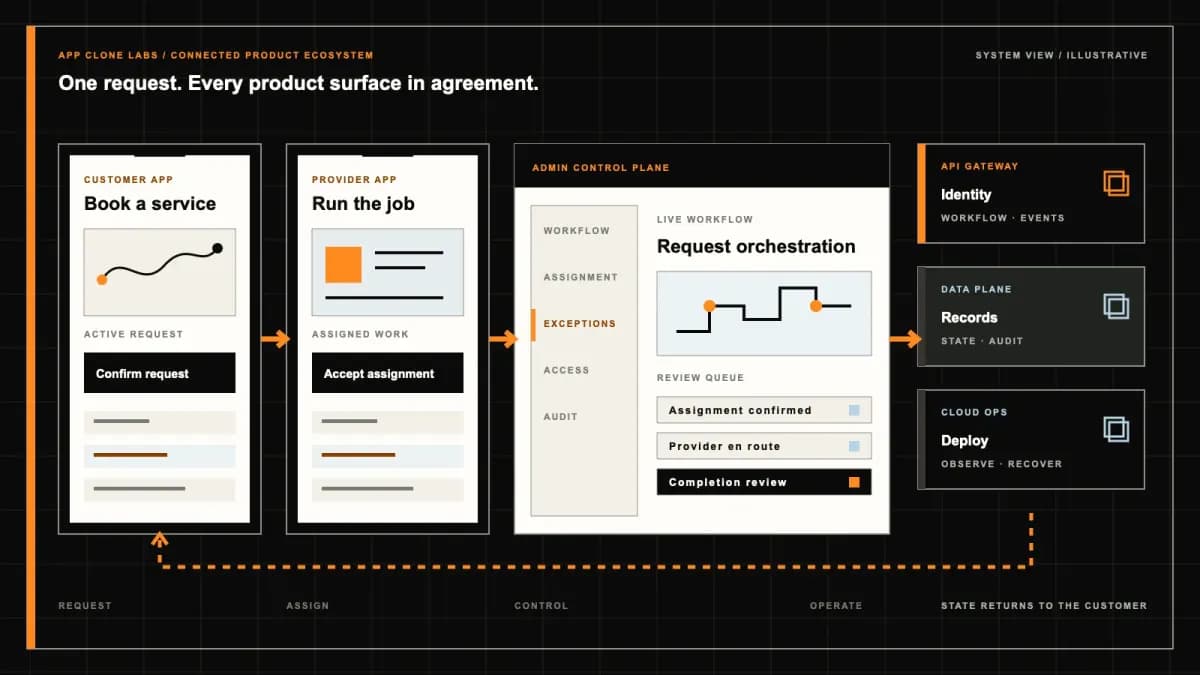
A super app provides a common entry point to independently governed service workflows such as mobility, delivery, commerce and professional bookings. This is original software scoped for an operator, not another company’s network, proprietary platform or licensed financial infrastructure. Shared identity and visual consistency can improve navigation, but they do not merge service obligations. Buyers should map operating responsibility before deciding which capabilities genuinely belong in the shared platform.
Define each module by the commitment it is allowed to create
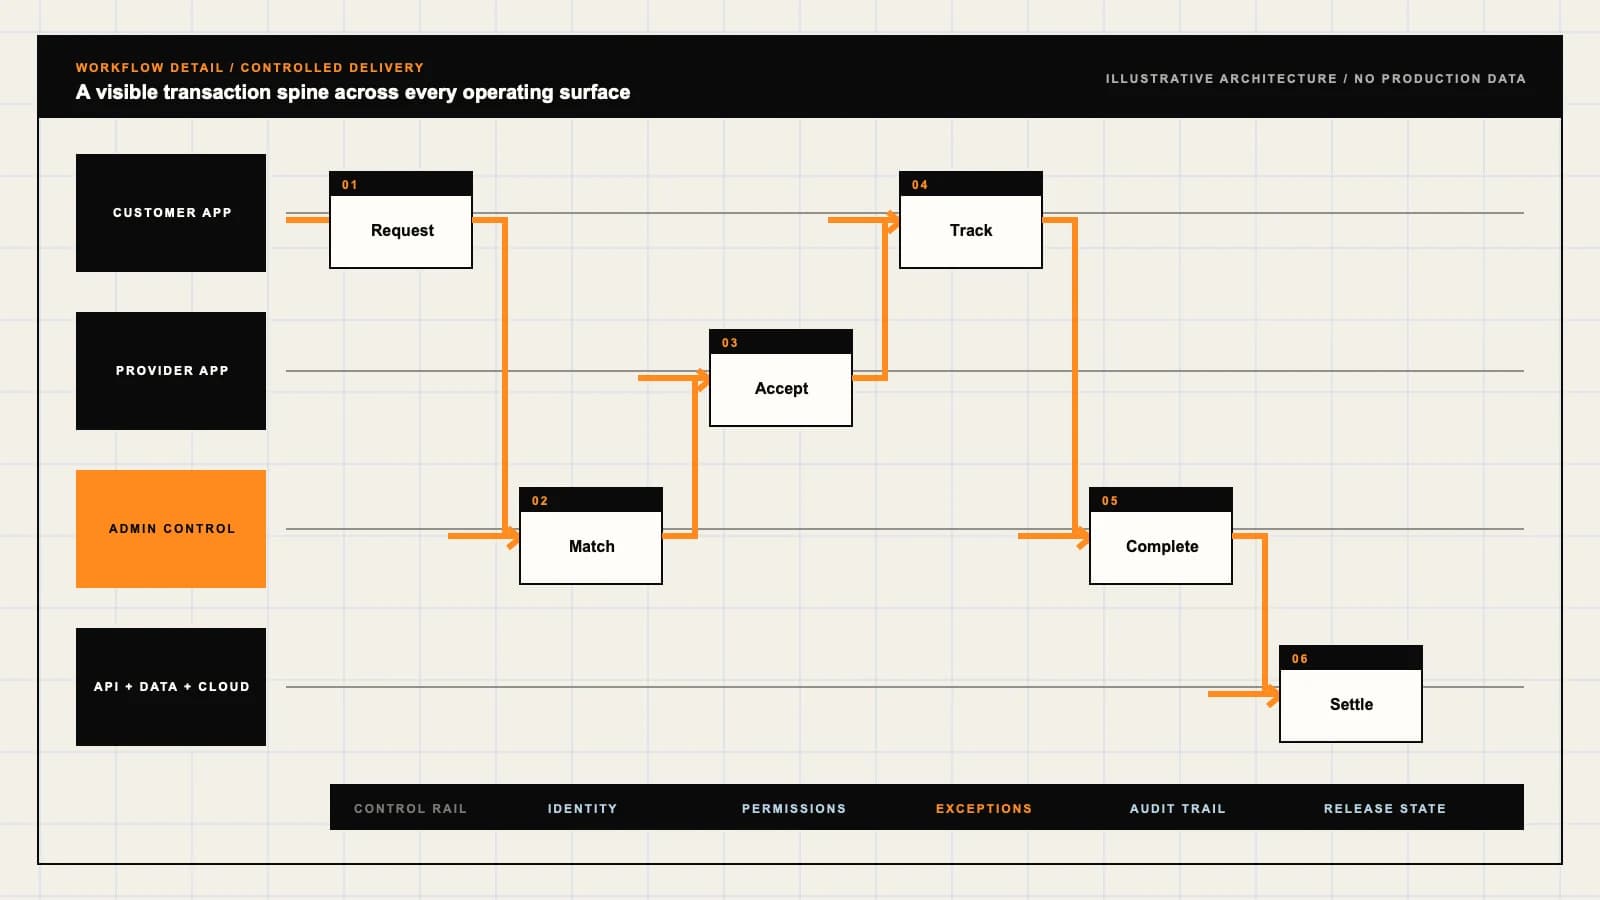
A ride commitment, merchant order and professional appointment have different actors, completion events and exception rules. Assign each module a clear domain boundary, accountable operator and authoritative transaction record. Shared discovery can link into those workflows without becoming the owner of every state change. Preserve service-specific terms and references so a customer or support agent can identify which obligation is being discussed even after moving between screens.
Avoid a universal status field that assumes accepted, completed and refunded mean the same thing everywhere. A merchant can accept an order before a courier is allocated; a ride completion can precede payment resolution. Document the events a module publishes and the actions other modules may request. Buyers should inspect these contracts using real exception examples rather than accepting a broad feature list that calls every workflow a booking.
Shared authentication must not become universal authorization
The OpenID Connect Core specification describes an identity layer for verifying an end user and communicating claims. It does not by itself grant permission to perform every action in every service. Use it as design guidance for reviewed identity integration, not evidence that a proposed platform already implements or has been certified against the standard.
After authentication, evaluate module eligibility and action permissions in context. A verified customer might be allowed to book a ride while still lacking access to a restricted product. A support employee authorized to view delivery evidence should not automatically see sensitive professional-service records. Keep token validation, account recovery and role changes within reviewed boundaries. Test revoked staff access and a stale client session so the interface cannot substitute an old menu state for current authority.
Reuse shared capabilities without creating hidden dependency chains
Identity, notifications, maps and search can serve several modules, but each creates a dependency whose failure needs an explicit response. Separate mandatory transaction checks from convenience features. A delayed notification should not cause the business state to disappear; failure of an essential eligibility check should not silently permit the action. Record what each module needs synchronously and what can recover later through a durable, observable process.
Start with the simplest architecture that supports the actual boundaries. A disciplined modular application may be appropriate before separate deployments are justified; microservices are not a prerequisite for a super app. Conversely, separate servers do not prove isolation if they share unrestricted credentials or exhaust one database pool. Document ownership, capacity assumptions and recovery behavior before choosing infrastructure. The buyer needs an understandable operating model, not a fashionable architecture label.
A busy service must not consume every module’s resources
Microsoft’s bulkhead architecture guidance explains partitioning resources to contain failure and discusses the associated overhead. This is a reference for evaluating isolation, not a performance result or a promise that all faults can be contained. Choose boundaries and mechanisms according to the product’s risks, deployment model and measured operating needs.
Specify dependency timeouts, concurrency limits and degraded behavior for the workloads that share resources. Keep repeated requests from a failing provider from crowding out unrelated work. Observability should identify the affected service and transaction rather than offer only a platform-wide green indicator. Rehearse an unavailable module and a saturated integration using controlled tests. Report what remained functional, what was intentionally refused and which recovery steps were required instead of claiming blanket resilience.
Shared payment presentation does not create a universal ledger
A saved payment choice can appear in several services while charges remain owned by different operators or provider arrangements. Give each financial action its module, transaction reference, reason and permitted actor. Keep authorization, capture, refund, settlement and unresolved results distinguishable. Do not use a refund from one service as an unexplained credit against another merely because the customer sees both transactions inside the same application.
Where membership, promotional credits or stored value crosses modules, define the issuer, eligible services, funding and reversal rules. Financial-service functionality needs appropriate licensed participation and specialist review; a wallet icon grants no authority. Payment callbacks must be idempotent and routed to the correct owner. Rehearse a delayed refund while an unrelated booking completes to confirm that reconciliation preserves both obligations without rewriting history or collecting the same amount twice.
Cross-module journeys need explicit partial-success rules
A customer may request a delivery after buying goods, but the commerce purchase and courier commitment remain separate events. Specify what happens if the second service refuses the request after the first succeeds. The customer should see the existing purchase, the failed delivery attempt and the available recovery choices. Avoid promising one atomic transaction where external providers and operating entities cannot actually support that guarantee.
Link related transactions with traceable references and define permitted compensating actions. A failed courier assignment does not automatically authorize cancellation of a merchant purchase or refund of every charge. Obtain consent for a revised option and preserve the original terms. Buyers should test partial success, duplicate handoff requests and an unavailable dependent module. Every unresolved outcome needs an owner even when several services participate in the same customer journey.